Executive Summary and Provider Overview
Quick-Reference Attributes
| Common Names | ZServers; XHost; XHOST Internet Solutions LP; zservers.ru |
|---|---|
| Node Type | Bulletproof Hosting Provider |
| Status | Disrupted, February 2025 |
| Entity Registration (ZServers) | Russia, Barnaul, Altai Krai |
| Entity Registration (XHOST LP) | United Kingdom, Limited Partnership (front company for ZServers) |
| Infrastructure Jurisdiction | Netherlands (primary, 127 servers seized Amsterdam); Russia, United States, Bulgaria, Finland (secondary, advertised) |
| Operator Location | Russia, Barnaul, Altai Krai (Mishin and Bolshakov, per sanctions and OSINT) |
| Active Period | ~2010 to February 2025 (approximately 15 years; Intel 471: "more than a dozen years") |
| Primary ASN | AS197414, De-registered (RIPE WHOIS record empty as of June 2026; last BGP announcement December 4, 2025; registered to XHOST Internet Solutions LP as of March 2025) |
| IP Ranges | 87.251.64.0/24 (XHOST); 185.170.144.0/24 (Vault Dweller OU, Estonia), 0 prefixes announced as of June 2026 |
| Abuse Contact | abuse@isxhost.com (shared across both ranges) |
| Confirmed Upstream Provider | Hostkey (Netherlands), confirmed via September 2024 data breach (Mishin account under real name) |
| Sanctions | OFAC CYBER3; UK FCDO Cyber Sanctions; AU DFAT, all February 11, 2025 |
| Primary Clients | LockBit, Conti, BianLian, Hunters International; Mallox, Dharma, Phobos, Globeimposter; IABs; darknet markets |
| On-Chain Activity | $5.2M+ documented (Chainalysis Reactor); cash-out via Garantex and no-KYC exchanges |
| Blocklist Status | Historically listed, Spamhaus SBL/abuse.ch probable; specific entry IDs not publicly enumerated |
| State Nexus Tier | Tolerated Safe Harbor (Tier 2 of 4) |
Overall Assessment
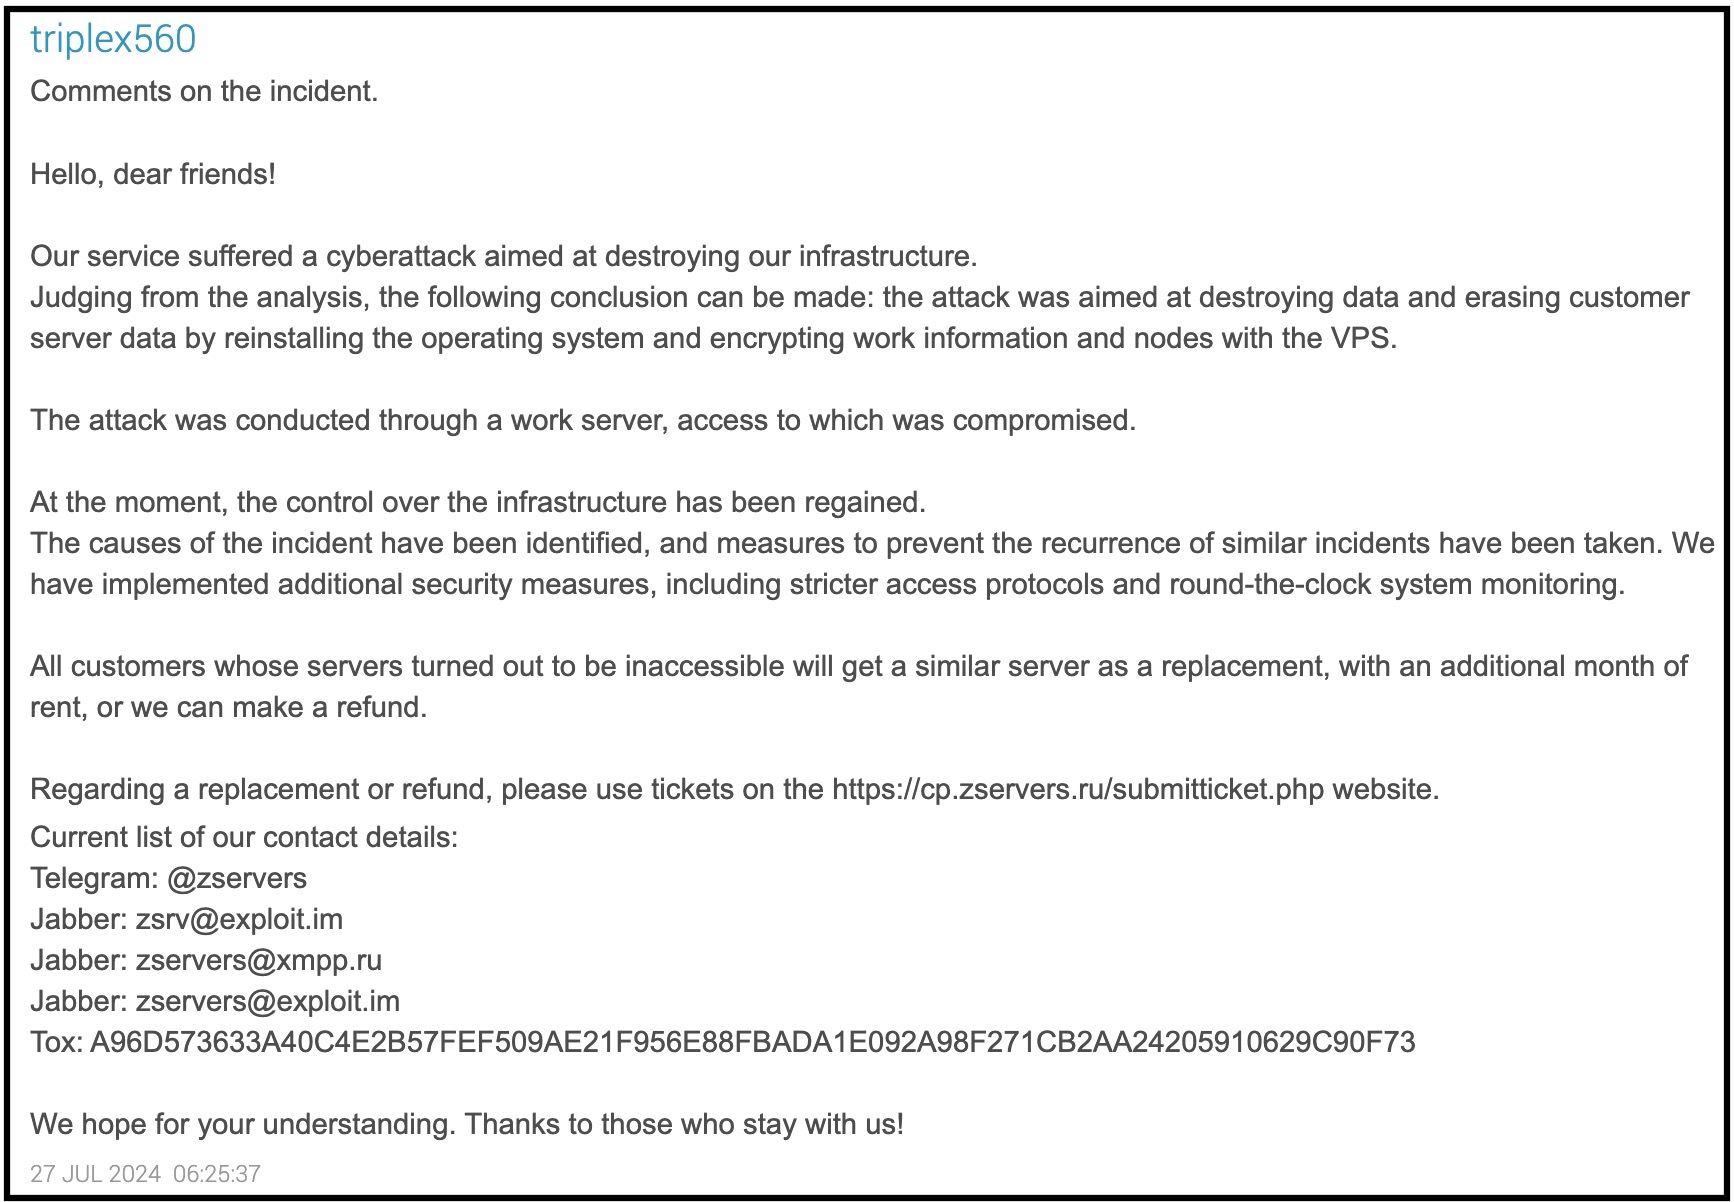
ZServers/XHost operated for approximately 15 years as one of Russia's most prominent bulletproof hosting providers, explicitly advertising crimeware-friendly services on Russian underground forums from at least 2010. Its primary administrator, Alexander Mishin (handle: triplex560), began advertising abuse-tolerant hosting on criminal forums with the zservers.ru domain circa 2010-2011; Intel 471 traces the persona to a forum post as early as January 2006. The provider's model centered on cryptocurrency-only anonymous payments, multi-jurisdiction hosting to resist law enforcement action, and a UK front company (XHOST Internet Solutions LP) to mediate relationships with Western data centers.
Coordinated US/UK/AU sanctions on February 11, 2025 and the Dutch National Police seizure of 127 Amsterdam servers on February 12-13, 2025 effectively dismantled its Western-facing infrastructure. Chainalysis documented at least $5.2 million in on-chain activity, with cash-outs through sanctioned exchange Garantex. Australia's Signals Directorate independently deleted 520 GB of Medibank health data stored on ZServers infrastructure. As of mid-2026, AS197414 remains registered to XHOST, the website was still online as of March 2025, and forum commentary predicted a rebrand, but no confirmed successor brand has been publicly identified.
Lineage and Organizational Heritage
Brands and Entity Structure
| Brand / Entity | Type | Role | Active Window | Confidence |
|---|---|---|---|---|
| ZServers / zservers.ru | Russia-based hosting company | Core BPH operation; primary entity | ~2010 to Feb 2025; residual post-takedown | Confirmed |
| XHOST Internet Solutions LP | UK Limited Partnership | Front/obfuscation layer for ZServers; holds AS197414; interfaces with EU data centers | Pre-2025 to sanctions Feb 11, 2025; ASN still registered March 2025 | Confirmed |
UK sanctions explicitly state XHOST was "established to support and obfuscate relevant cyber activity by ZSERVERS, a Russian-based provider of bulletproof hosting." [3]
Predecessor Lineage
Analyst Inference No public evidence ties ZServers to prior-generation BPH brands such as Maxided or Yalishanda. Government designations treat ZServers as a distinct provider. The triplex560 persona's earliest confirmed hosting advertisement dates to August 2010 on xeksec.com; Intel 471 assessed "more than a dozen years" of operation from 2025. Founding circa 2010-2012 is most consistent with available evidence. [1]
Evidence Pillars
Confirmed Clear continuity between ZServers and XHOST Internet Solutions LP: shared AS197414, shared abuse contact abuse@isxhost.com, 127 servers in Amsterdam confirmed as ZServers/XHost infrastructure by Dutch police and international LE statements. [1][2][3][5]
Confirmed Mishin and Bolshakov identified as administrators by OFAC, UK, and AU. Intel 471 independently corroborated Mishin's identity via social media, leaked database records (SDEK, Pikabu), WHMCS account, GitHub, and Skype IDs: all converging on Mishin Alexander Igorevich in November 2024. Forum IPs traced to Barnaul/Biysk, Altai Territory. [1]
Confirmed OFAC listed one BTC address for Mishin and three digital currency addresses for ZServers. Chainalysis confirmed $5.2M+ on-chain activity with direct exposure to LockBit, Mallox, Dharma, Phobos, Globeimposter, IABs, and darknet markets. Cash-out via Garantex confirmed. [6][7]
Operator Profiles
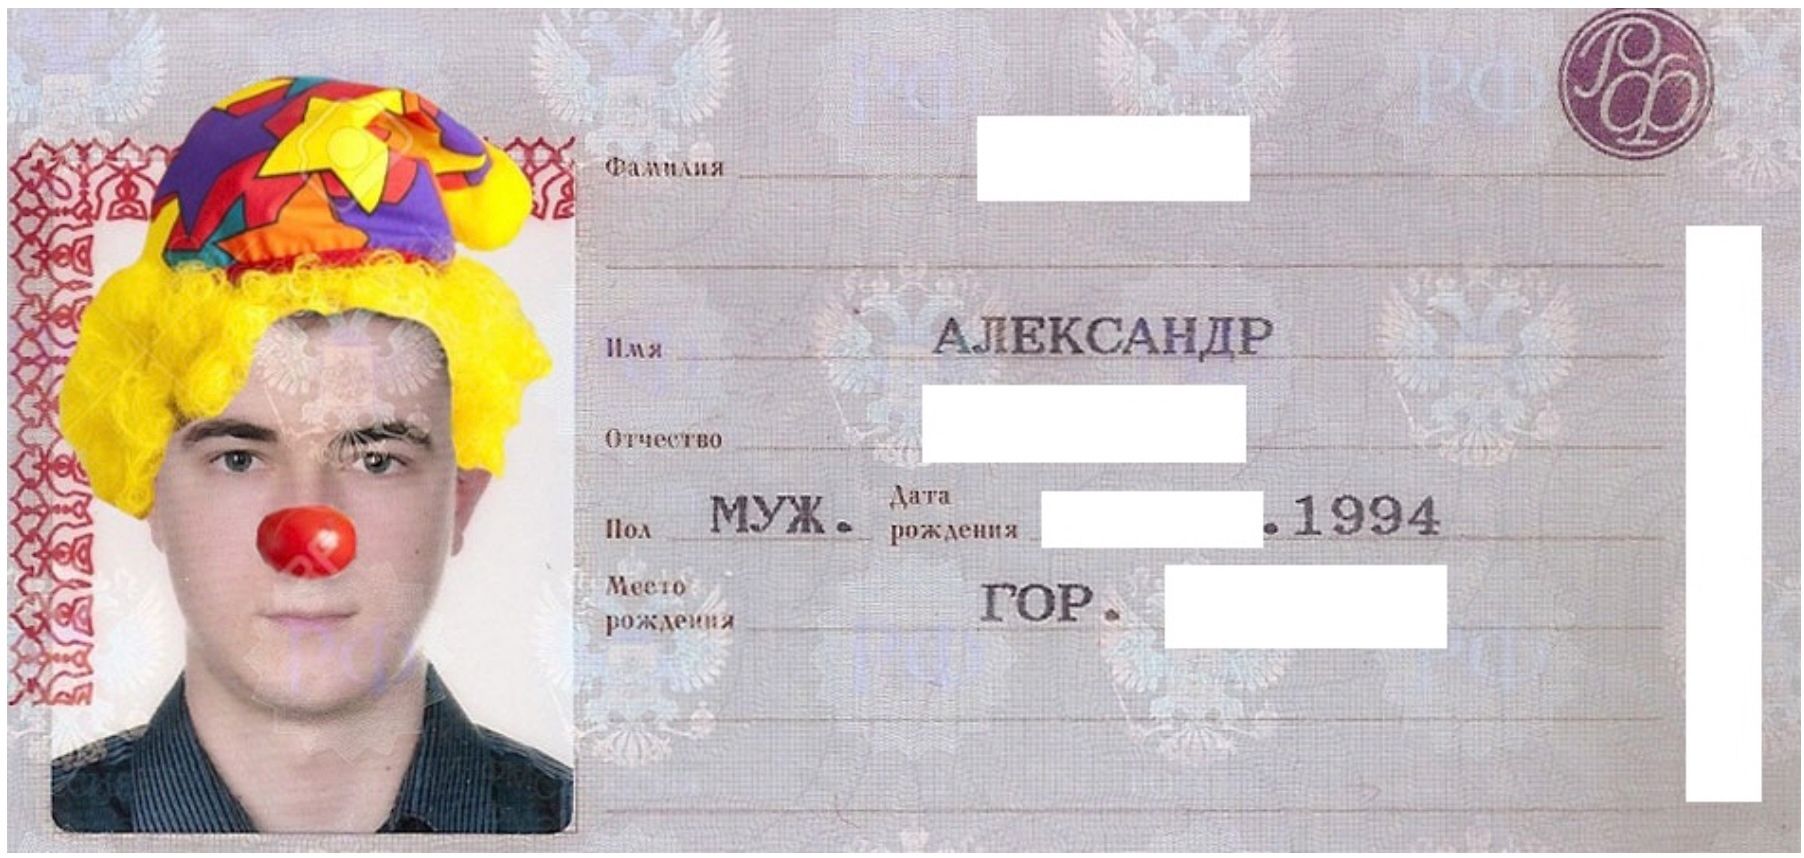
2.1 Alexander Igorevich Mishin
| Full Name | Mishin, Alexander Igorevich (Мишин Александр Игоревич) |
|---|---|
| Date / Place of Birth | 18 March 1994, Altai Krai, Russia |
| Address | Ul. Yubileynaya, D. 32, Barnaul, Altai Krai, Russia |
| Assessed Location | Russia (Barnaul / Altai Krai), assessed; not arrested or extradited |
| Handles / Aliases | triplex560, alex560560, james1789, ZserverS, sasha-brn, PIPPIN James, KLICHKO Ivan P. |
| Role | Administrator; personally managed advertising on criminal forums and cryptocurrency payments |
| Forum History | zloy.bz from Jan 2006; xeksec.com Aug 2010 (verbatim ad); Antichat, Exploit, XSS, proxy-base.com, hackersoft.ru (ongoing to Feb 2025) |
| BTC Address (OFAC) | 3FfRvC3kSo2SxiQe5e7SSuNdegwgq8iusL |
| Sanctions | OFAC CYBER3 (Feb 11, 2025); UK FCDO Cyber Sanctions (Feb 11, 2025); AU DFAT (Feb 11, 2025) |
| Legal Status | Sanctioned; at large in Russia; no public arrest or criminal indictment confirmed |
2.2 Aleksandr Sergeyevich Bolshakov
| Full Name | Bolshakov, Aleksandr Sergeyevich (Большаков Александр Сергеевич) |
|---|---|
| Date / Place of Birth | 23 July 1994, Semipalatinsk, Kazakhstan |
| Address | 97 Vzletnaya, Apt 170, Barnaul 656067, Russia |
| Assessed Location | Russia (Barnaul), assessed; not arrested |
| Handles / Aliases | aaelbas, wtlfnt |
| Role | Owner per AU designation; implicated in 2023 IP reassignment episode (LockBit client reprotection) |
| Sanctions | OFAC CYBER3; UK FCDO; AU DFAT, all February 11, 2025 |
| Legal Status | Sanctioned; at large in Russia; no public arrest |
2.3 Additional Sanctioned Individuals (UK / AU Only)
UK FCDO designated six individuals total; AU DFAT designated five. Four beyond Mishin and Bolshakov:
| Name | Sanctioning Authorities | Notes |
|---|---|---|
| Ilya Sidorov | UK FCDO, AU DFAT | Employee; specific role not publicly detailed |
| Dmitriy Bolshakov | UK FCDO, AU DFAT | Employee; relation to Aleksandr Bolshakov unclear from public sources |
| Igor Odintsov | UK FCDO, AU DFAT | Employee; specific role not publicly detailed |
| Vladimir Ananev | UK FCDO only | Employee; specific role not publicly detailed |
Credible Full roles for these four individuals are an intelligence gap. Complete UK and AU sanctions notices may contain additional detail not indexed in public sources.
Disputed Assessments
No vendor disputes identified regarding ZServers' core identity, the XHOST front relationship, or Mishin/Bolshakov attribution. Successor infrastructure remains unconfirmed.
Operational and Business Model
Service Model
ZServers operated as a full-service bulletproof hosting provider: leasing dedicated servers, VPS instances, and IP address blocks to cybercriminal clients on an anonymous, cryptocurrency-only basis. Services explicitly included C2 hosting, ransomware operational portals, botnet C2, malware distribution, and phishing/fraud infrastructure. The provider explicitly guaranteed protection from law enforcement and abuse reporters, and advertised that criminals were welcome.
Verbatim Advertising Copy
Onboarding and Vetting
Open signup with high anonymity: cryptocurrency payment, minimal or no KYC, remote provisioning. Forum-based advertising on Exploit, XSS, and Antichat constitutes implicit vetting, clientele self-selects from established underground forums. No invite-only or referral requirements confirmed. Full onboarding workflow details are an intelligence gap.
Pricing
No confirmed public price list. Homepage described servers in five countries with support, equipment, and custom configuration, implying tiered geographic and hardware offerings. Monthly subscription model inferred from BPH standard practice. Early 2010 ads listed WebMoney as a payment method; later operations shifted to cryptocurrency-only. Specific package names and prices are an intelligence gap.
Reseller Chain and Front Company
XHOST Internet Solutions LP (UK) functioned as ZServers' obfuscation and interface layer with Western infrastructure, a legal-entity wrapper used to contract with European data centers and handle formal correspondence. UK sanctions: XHOST was "established to support and obfuscate relevant cyber activity by ZSERVERS." [3]
The September 2024 data breach confirmed Mishin held a Hostkey (Netherlands) reseller account under his real name, confirming Hostkey as at least one upstream provider from which ZServers resold capacity. No additional named sub-reseller brands documented. This is an intelligence gap.
Abuse-Handling and LE Posture
Explicitly classified by OFAC as a provider that "ignores or evades law enforcement requests" and provided "specialized servers designed to resist law enforcement actions." [4][6]
A 2023 exception demonstrates selective, deceptive responsiveness: following a complaint from a Lebanese company about a ZServers-hosted LockBit IP, Mishin instructed Bolshakov to change the IP address, then falsely told the company the original IP was cut off, while secretly reassigning a new IP to the LockBit client. This preserves upstream ISP relationships without actually cooperating. [1][4]
OPSEC Posture
Anonymous cryptocurrency payments; pseudonymous forum advertising; UK front company for EU contracts; multi-jurisdiction infrastructure. Client communication likely via ticket panels (WHMCS-style), Jabber/XMPP, and Telegram. Specific panel domains and Telegram handles are an intelligence gap. OPSEC failed significantly in September 2024 (data breach exposing 9,500 client records and Mishin's upstream accounts).
Technical Capabilities and Infrastructure Footprint
ASN Registration and IP Ranges
| ASN | Registered Name | IP Range | Abuse Contact | Status (March 2025) |
|---|---|---|---|---|
AS197414 | XHOST Internet Solutions LP (registered to XHOST as of March 2025; RIPE WHOIS record now empty) | 87.251.64.0/24 | abuse@isxhost.com | De-registered |
AS197414 | XHOST Internet Solutions LP (via Vault Dweller OU, Estonia) | 185.170.144.0/24 | abuse@isxhost.com | Last announced Dec 4, 2025 |
AS59753 | XHOSTIS-AS (Vault Dweller OU, ORG-VDO2-RIPE, maintainer MNT-VLTDWELLER) | none announced since Nov 2022 | Vault Dweller abuse role | De-registered (no aut-num object, 29 Oct 2026) [17][18] |
AS200730 | "ISAEV ISAEV Igor" (holder per RIPEstat, June 2026) | 87.251.64.0/24 (Jun 2025 to Jul 2026) | none on record | De-registered last announcement 26 Jul 2026; no aut-num object 29 Oct 2026 [18] |
Residual XHOST Objects in the RIPE Database (29 October 2026)
Confirmed The XHOST maintainer ISXHOST-MNT (created 17 Feb 2023, update address ripe@isxhost.com) still exists, together with its contact person MW11280-RIPE "Mark Williams", Suite 6060, 128 Aldersgate Street, Barbican, London (a virtual-office address), phone +44 20 8157 7196. The maintainer still controls two reverse-DNS domain objects: 76.66.80.in-addr.arpa (for 80.66.76.0/24, created 4 Aug 2023, nameservers ns1/ns2.hostkey.com) and 66.66.80.in-addr.arpa (for 80.66.66.0/24, created 17 Feb 2024, nameservers creanova.org). Both /24s, like the former XHOST prefix 87.251.64.0/24, sit inside allocations held by the Omsk-based individual LIR Aleksandr Valerevich Mokhonko (ORG-PMAV1-RIPE, maintainer ru-avm-1-mnt; allocations 80.66.64.0 to 80.66.89.255 and 87.251.64.0/20). Today 80.66.76.0/24 is announced by AS213010 (Gening Nikita Dmitrievich) and 80.66.66.0/24 by AS209702 (Soldatov Aleksey Valerevich), both Russian individual ASNs under the same LIR. Analyst Inference The Hostkey nameservers on an XHOST-managed reverse zone corroborate the Hostkey upstream relationship documented from the 2024 breach; the Mokhonko LIR is the common sponsoring LIR behind XHOST's old and residual address space and is a Russian-jurisdiction node with no Western lever. The same LIR's customer list includes an individual registrant in Barnaul, Altai Territory, the region to which Intel 471 traced Mishin's forum logins; this is a geographic coincidence and is not treated as evidence. [1][18]
Confirmed RIPE RIS and WHOIS queried June 2026: AS197414 WHOIS record is empty (no aut-num object exists); 0 of 327 RIS peers see any announcement; 0 prefixes, 0 IPs advertised. The ASN has been de-registered. Last observed BGP announcement: December 4, 2025, prefix 185.170.144.0/24: approximately 10 months after sanctions. As of March 2025 the ASN was still registered to XHOST Internet Solutions LP (Intel 471 WHOIS verification); it was de-registered sometime between March and December 2025. First seen active: May 28, 2011. Full historical RIPE/ARIN allocations and additional ASNs are an intelligence gap. [1]
Both previously XHOST-associated IP ranges were actively routed as of June 5, 2026 by ASNs other than AS197414. Re-checked 29 October 2026 against the RIPE database and RIPEstat: [18]
87.251.64.0/24: the inetnum is now ASSIGNED PA to "Isaev Igor Maratovich" (netname ISAEV, country PL, maintainers ru-avm-1-mnt and ISAEV-MNT, object modified 5 Mar 2026) inside the Mokhonko LIR allocation 87.251.64.0/20. AS200730 stopped announcing it on 26 July 2026 and has no RIPE object; since a route object created 24 July 2026 the prefix is announced by AS212835 (SHESTERNIN-AS, Shesternin Vladimir Anatolievich), another individual ASN under the same LIR. Analyst Inference Two successive individual-name ASNs under one Russian LIR holding the ex-XHOST prefix looks like LIR-level reallocation of leased space rather than operator reconstitution; no link to Mishin or Bolshakov is established.
185.170.144.0/24: the June 2026 reading ("no assessed connection") was incomplete. The inetnum is an ALLOCATED PA block registered to Vault Dweller OU (ORG-VDO2-RIPE, Tallinn, Estonian reg-nr 14752442; maintainer MNT-VLTDWELLER; netname EE-VLTDWELLER-20200113; modified 20 Feb 2026) with mnt-lower and mnt-routes delegated to the IP broker interlir-mnt (InterLIR). The route object (created 17 Apr 2026, maintained by InterLIR) points at AS50053 (VDSKA-AS, Anton Levin), so AS50053 is a lessee of Vault Dweller space via InterLIR, not an unrelated new holder. Vault Dweller OU is the Estonian entity behind the DEDBROPRO profile and the former registrant of AS59753 (XHOSTIS-AS); see Section 09. [17][18]
Physical Infrastructure
Primary EU infrastructure concentrated at Paul van Vlissingenstraat colocation facility, Amsterdam, Netherlands, 127 servers seized here by Dutch National Police on February 12-13, 2025. Additional servers advertised in Russia, United States, Bulgaria, and Finland, suggesting leased rack or dedicated server arrangements at facilities in those countries. Whether seizures occurred outside the Netherlands is not confirmed.
Upstream Transit Provider Chain
The September 2024 data breach confirmed Mishin held a reseller account at Hostkey (Netherlands-based dedicated server provider) registered under his real name, establishing Hostkey as at least one upstream provider from which ZServers leased and resold capacity. [1]
Credible Two further Hostkey indicators found 29 October 2026: the XHOST-maintained reverse zone for 80.66.76.0/24 delegates to ns1/ns2.hostkey.com (RIPE domain object, Aug 2023), and the Vault Dweller OU block 91.236.186.0/24 (registered 25 Mar 2026) is announced today by HOSTKEY B.V. (AS57043). Sponsoring LIR for the XHOST prefix and residual ranges: Aleksandr Valerevich Mokhonko, Omsk (ORG-PMAV1-RIPE), a Russian individual LIR. [18]
No documented de-peering events prior to February 2025 appear in public reporting. The coordinated action went directly to sanctions and physical seizure rather than relying on upstream de-peering. Additional upstream ISPs providing transit to the Amsterdam facility are not documented in open sources. This is an intelligence gap requiring BGP historical data or network operator community records. No upstream de-peering events documented.
Resilience Features
Multi-jurisdiction advertising (five countries) as classic resilience pattern. OFAC: "specialized servers designed to resist law enforcement actions." Leased capacity from multiple upstream providers (Hostkey confirmed; others unconfirmed). IP rotation demonstrated in the 2023 LockBit episode. Fast-flux or anycast operations not documented in open sources.
Hosted Activity Types
| Activity Type | Evidence Basis | Confidence |
|---|---|---|
| Ransomware C2 and operational infrastructure (LockBit) | OFAC, UK FCDO, AU DFAT, Chainalysis, TRM Labs, Reuters, The Record, LockBit affiliates explicitly cited using ZServers for chat servers and C2 | Confirmed |
| Ransomware infrastructure (Conti) | Dutch National Police press statements; SecurityWeek; SecurityAffairs | Confirmed |
| Data exfiltration / extortion site hosting | ASD found Medibank data (520GB) on ZServers; Intel 471: Hunters International ransom note and exfil file list found in September 2024 ZServers data breach | Confirmed |
| Botnet C2 | Dutch National Police; Bleeping Computer; Cybernews; multiple press sources | Confirmed |
| Malware distribution (loaders, stealers, generic) | Dutch police; SecurityOnline; SecurityAffairs; multiple outlets | Confirmed |
| Ransomware infrastructure (BianLian, Hunters International) | Intel 471; AU DFAT Minister statement (BianLian); Infopercept (both) | Credible |
| Phishing / fraud infrastructure | 2010 ad explicitly listed phishing as allowed; LegalData; LE characterizations | Credible |
| DDoS-for-hire | No direct references in open sources | Analyst Inference |
Blocklist Standing
| Source / List | Status | Notes |
|---|---|---|
| Spamhaus SBL | Historically Listed (Probable) | Multiple sources characterize ZServers as BPH used for malware, botnets, and ransomware, consistent with SBL criteria. Specific SBL entry IDs, first-listing dates, and delisting events not documented in open sources. No public dispute filings by ZServers. |
| Spamhaus CBL / XBL | Historically Listed (Probable) | IP ranges associated with documented botnet C2. Specific entries not publicly enumerated. |
| Spamhaus DROP / eDROP | Probable | AS197414 and IP ranges consistent with DROP criteria (cybercrime-leased netblocks). Specific DROP list entries not confirmed in open sources. |
| abuse.ch Feodo Tracker | Historically Listed (Probable) | Documented ransomware C2 and botnet hosting makes Feodo Tracker entries for ZServers IPs likely. Not specifically cited in open-source reporting. |
| abuse.ch URLhaus | Historically Listed (Probable) | Malware distribution function suggests URLhaus entries for hosted payload URLs. Not publicly enumerated. |
| abuse.ch MalwareBazaar | Unknown | No direct references to MalwareBazaar entries in available reporting. |
| Firehol Level 1/2 | Probable | As an aggregator, Firehol almost certainly included ZServers-associated IPs given documented activity. Not specifically confirmed in reporting. |
Summary: ZServers/XHost IP space is widely characterized as malicious infrastructure associated with ransomware, botnets, and malware distribution. Historical listings on Spamhaus SBL and abuse.ch are highly probable given the documented activity types, but specific entry IDs, first-listing dates, and delisting events are not enumerated in available open-source reporting. No evidence of ZServers challenging or disputing blocklist entries; operational posture was systematic non-cooperation.
Known Weaknesses Exploited
Concentration of 127 servers in a single Amsterdam facility created a physical single point of failure exploited by Dutch police in February 2025. The XHOST UK front created a sanctionable legal hook in a Western jurisdiction. Multi-jurisdiction hosting provided resilience against single-country action but not against coordinated three-country sanctions plus a physical seizure in 48 hours. Mishin's Hostkey account under his real name, revealed in the September 2024 breach, exposed upstream relationships and contributed to OPSEC failure.
Financial Infrastructure
Payment Methods
ZServers accepted payments predominantly via cryptocurrency for anonymous client signups. Dutch police and multiple outlets confirm "cybercriminals could purchase services anonymously, by paying with cryptocurrency." The 2010 ad copy listed WebMoney as an accepted method, suggesting early e-money use before full cryptocurrency adoption. No card payments or fiat bank transfers referenced in post-2020 reporting.
Wallet Clusters and Designated Addresses
| Address | Currency | Designation | Source |
|---|---|---|---|
3FfRvC3kSo2SxiQe5e7SSuNdegwgq8iusL | BTC (XBT) | Mishin (individual) | OFAC SDN, Feb 11, 2025 |
| 3 additional addresses (full addresses not publicly indexed) | Digital currency | ZServers entity designation | OFAC SDN, Feb 11, 2025; confirmed by TRM Labs, Chainalysis |
On-Chain Activity: Three-Phase Laundering Model
Phase 1: Acquisition (Service Fees Inbound)
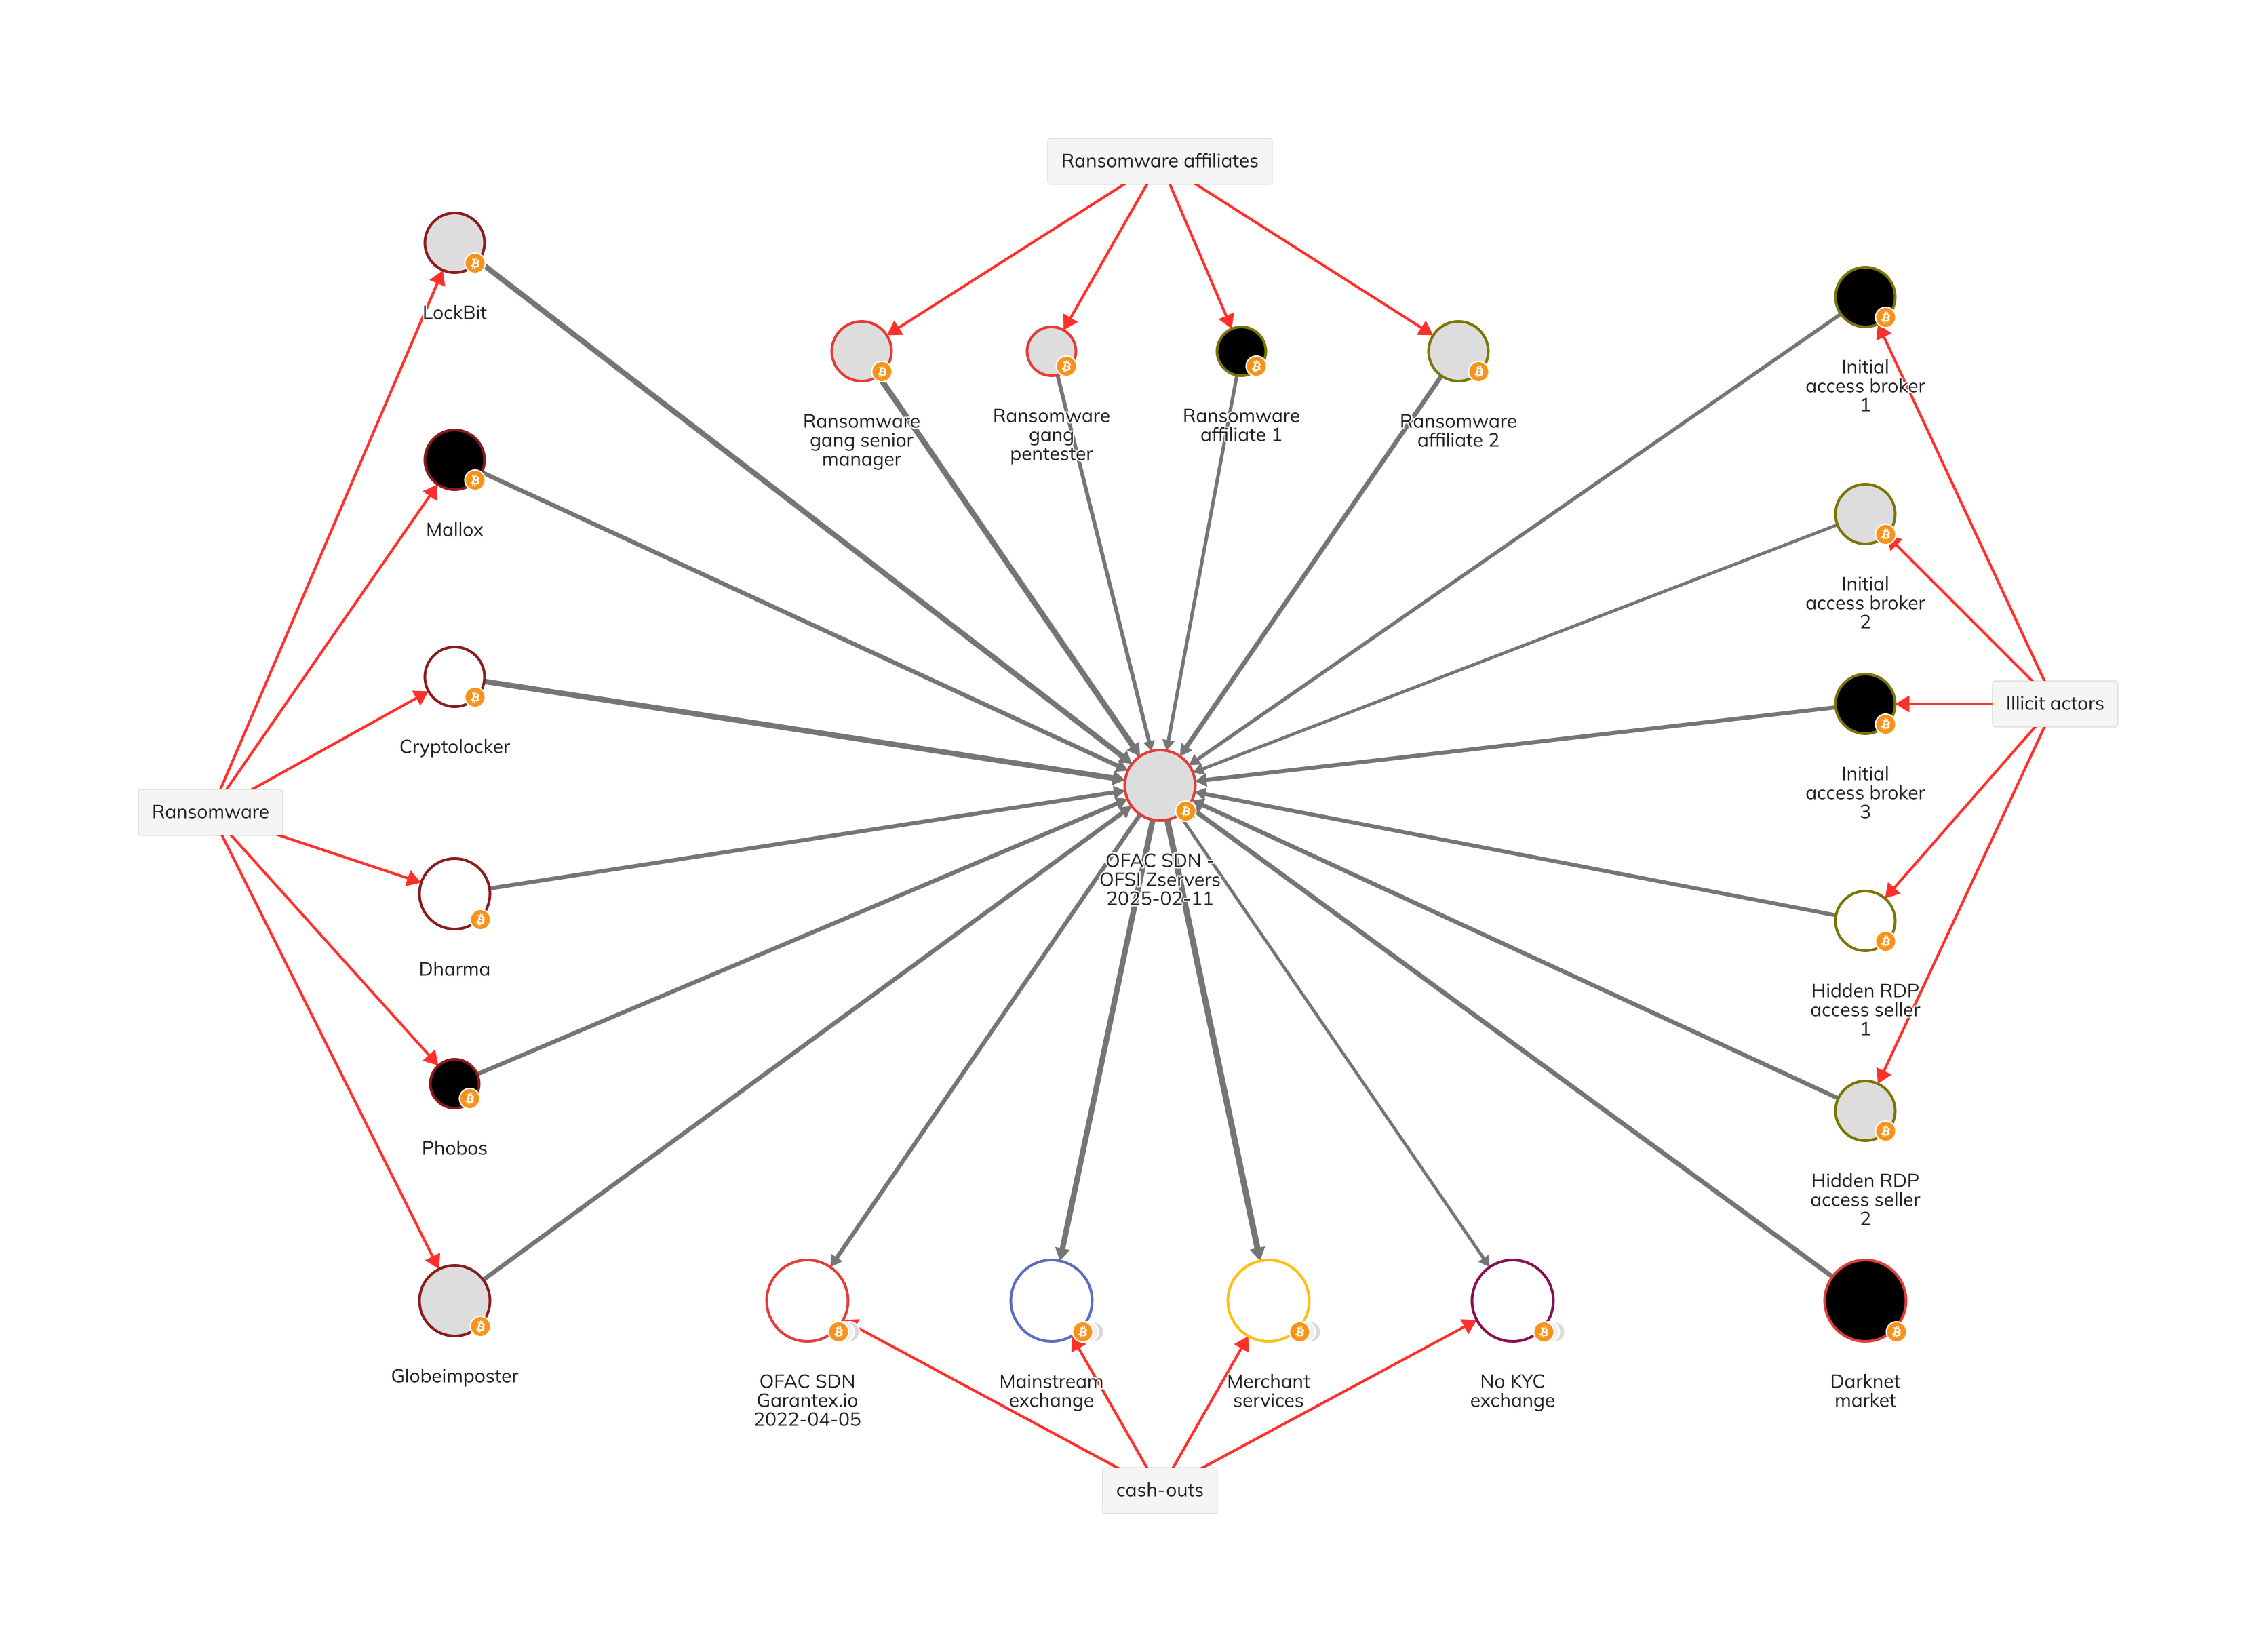
ZServers-linked wallets received hosting fee payments from ransomware affiliates and other criminal clients. Chainalysis confirmed inbound payments from LockBit affiliates, Mallox, Cryptolocker, Dharma, Phobos, and Globeimposter, as well as IABs and darknet markets. Documented on-chain activity: at least $5.2 million. [6][7]
Phase 2: Layering
Funds moved through intermediary wallets. Chainalysis documented movement to mixing services and high-risk exchanges. TRM Labs noted chain-hopping behavior consistent with standard ransomware ecosystem layering. Specific mixing services or cross-chain bridges not named in public reporting. [6][7]
Phase 3: Extraction (Cash-Out)
Chainalysis confirmed cash-out at: (1) Garantex, Russia-based exchange sanctioned by OFAC in 2022 for AML non-compliance; (2) merchant services providers; (3) no-KYC exchanges. The Garantex link places ZServers within the broader sanctioned Russian financial infrastructure cluster. [6][7]
Garantex was taken down on March 6, 2025, 23 days after ZServers sanctions: by US Secret Service, German BKA, and Finnish law enforcement. Domain seized; $26M in cryptocurrency frozen; two administrators indicted (Aleksej Besciokov and Aleksandr Mira Serda). Successor exchange Grinex created immediately post-seizure; OFAC designated Grinex; Grinex suspended operations April 16, 2026. The Garantex cash-out flows documented by Chainalysis occurred prior to the March 2025 seizure and represent historical activity, not a current operational route.
Sanctions and Risk Designations
| Authority | Program | Date | Entities Designated | Basis |
|---|---|---|---|---|
| OFAC (US) | CYBER3 / SDN | Feb 11, 2025 | ZServers; Mishin; Bolshakov; 4 crypto addresses | Materially assisted LockBit ransomware operations |
| UK FCDO | Cyber Sanctions Regime | Feb 11, 2025 | ZServers; XHOST LP; 6 individuals | "Key component of Russia's cybercrime supply chain"; LockBit attacks against UK organizations including hospitals |
| AU DFAT | Autonomous Cyber Sanctions | Feb 11, 2025 | ZServers; 5 individuals | BPH for BianLian; hosted Medibank stolen data (Oct 2022); first Australian sanctions against a hosting entity |
Client Profile and Hosted Operations
Crimeware Verticals by Evidence Tier
| Category | Named Clients | Evidence Basis | Classification |
|---|---|---|---|
| Ransomware RaaS (LockBit) | LockBit 2.0 and 3.0 affiliates | OFAC, UK FCDO, AU DFAT, Chainalysis, TRM Labs, Reuters, The Record | Confirmed |
| Ransomware RaaS (Conti) | Conti | Dutch National Police press statements; SecurityWeek; SecurityAffairs | Confirmed |
| Botnets | Not named | Dutch National Police; Bleeping Computer; Cybernews; multiple outlets | Confirmed |
| Malware distribution | Not named | Dutch police; SecurityOnline; SecurityAffairs | Confirmed |
| Ransomware (BianLian) | BianLian | Intel 471; AU DFAT Minister statement (Medibank context); Infopercept | Credible |
| Ransomware (Hunters International) | Hunters International | Intel 471 data breach analysis (ransom note in ZServers data); Infopercept | Credible |
| Multi-family ransomware (Chainalysis cluster) | Mallox, Cryptolocker, Dharma, Phobos, Globeimposter | Chainalysis Reactor on-chain payment tracing, direct payments to ZServers designated wallets Single Source | Credible |
| Initial Access Brokers | Not named | Chainalysis on-chain exposure data Single Source | Credible |
| Darknet markets | Not named | Chainalysis on-chain exposure data Single Source | Credible |
| Phishing / fraud | Not named | 2010 ad explicitly listed phishing as allowed; LegalData; LE characterizations | Credible |
Client Geography
Infrastructure concentrated in the Netherlands with secondary nodes in Russia, US, Bulgaria, and Finland. Clients target organizations globally. No CIS exclusion clause documented, ZServers appears to have operated without geographic restrictions on victims. UK FCDO cited attacks against UK hospitals as a direct use case. AU DFAT cited Medibank Private (October 2022, Australia's largest healthcare breach).
Notable Hosted Cases
ASD assessed ZServers infrastructure was used to store approximately 520 GB of data stolen in the October 2022 Medibank Private extortion attack. Attacker Aleksandr Ermakov (sanctioned January 2024, arrested by Russia) was attributed to the REvil ecosystem. ASD conducted an offensive cyber operation deleting the stolen data from ZServers' servers. ASD Director-General publicly cited this as part of ASD deleting up to 250 TB of stolen data from adversary systems globally. [1]
ZServers leased IP addresses and servers to LockBit affiliates for C2, victim communication portals, and operational infrastructure. OFAC explicitly designated ZServers for "materially assisting LockBit ransomware operations." UK FCDO cited LockBit affiliates using ZServers to launch attacks against UK organizations. [4][3]
State Nexus Assessment
Assessment: Tier 2: Tolerated Safe Harbor
The Russian state is assessed to be aware of ZServers' operations and to have refrained from enforcement or prosecution of its operators, despite 15 years of operation and extensive international notoriety. This constitutes tolerated safe harbor. No public evidence supports active operational cooperation, tasking, or direct protection beyond passive non-enforcement.
Entity headquartered in Barnaul, Russia; primary operators are Russian nationals in Barnaul; primary victims are Western organizations. Despite coordinated US/UK/AU sanctions and a high-profile Dutch takedown in February 2025, no Russian criminal proceedings against ZServers, Mishin, or Bolshakov appear in open sources. The US State Department explicitly criticized Russia in its February 2025 sanctions announcement, writing that Russia "continues to offer safe harbor for cybercriminals where groups are free to launch and support ransomware attacks against the United States and its allies and partners." [1]
Negative Evidence (Tier 3/4 Not Supported)
- No documented use of ZServers for Russian state espionage (GRU/FSB) campaigns
- No leaked communications showing direct tasking from Russian security services
- No explicit legal immunity or cooperation agreements referenced in any sanctioning government material
- No attribution of ZServers to named state-sponsored threat actor groups (APT28, APT29, Sandworm, etc.)
Analyst Inference The possibility that classified IC holdings contain Tier 3/4 evidence cannot be excluded but is not supported by available open-source reporting.
Jurisdictional Separation
This separation enabled Western authorities to act aggressively against infrastructure (Dutch seizure) and finances (trilateral sanctions) while primary operators remained in Russia outside arrest range. This is a deliberate and common BPH pattern.
Law Enforcement and Regulatory Response
Arrests, Indictments, Criminal Charges
As of mid-2026, no US DOJ indictment, UK CPS charges, or Dutch criminal charges against ZServers operators are confirmed in open sources. Mishin and Bolshakov are sanctioned but at large in Russia. Intel 471 notes that sealed indictments may exist, US prosecutors frequently seal grand jury indictments until arrest, making international travel risky for sanctioned actors. No public confirmation of criminal charges. [1]
Infrastructure Seizures
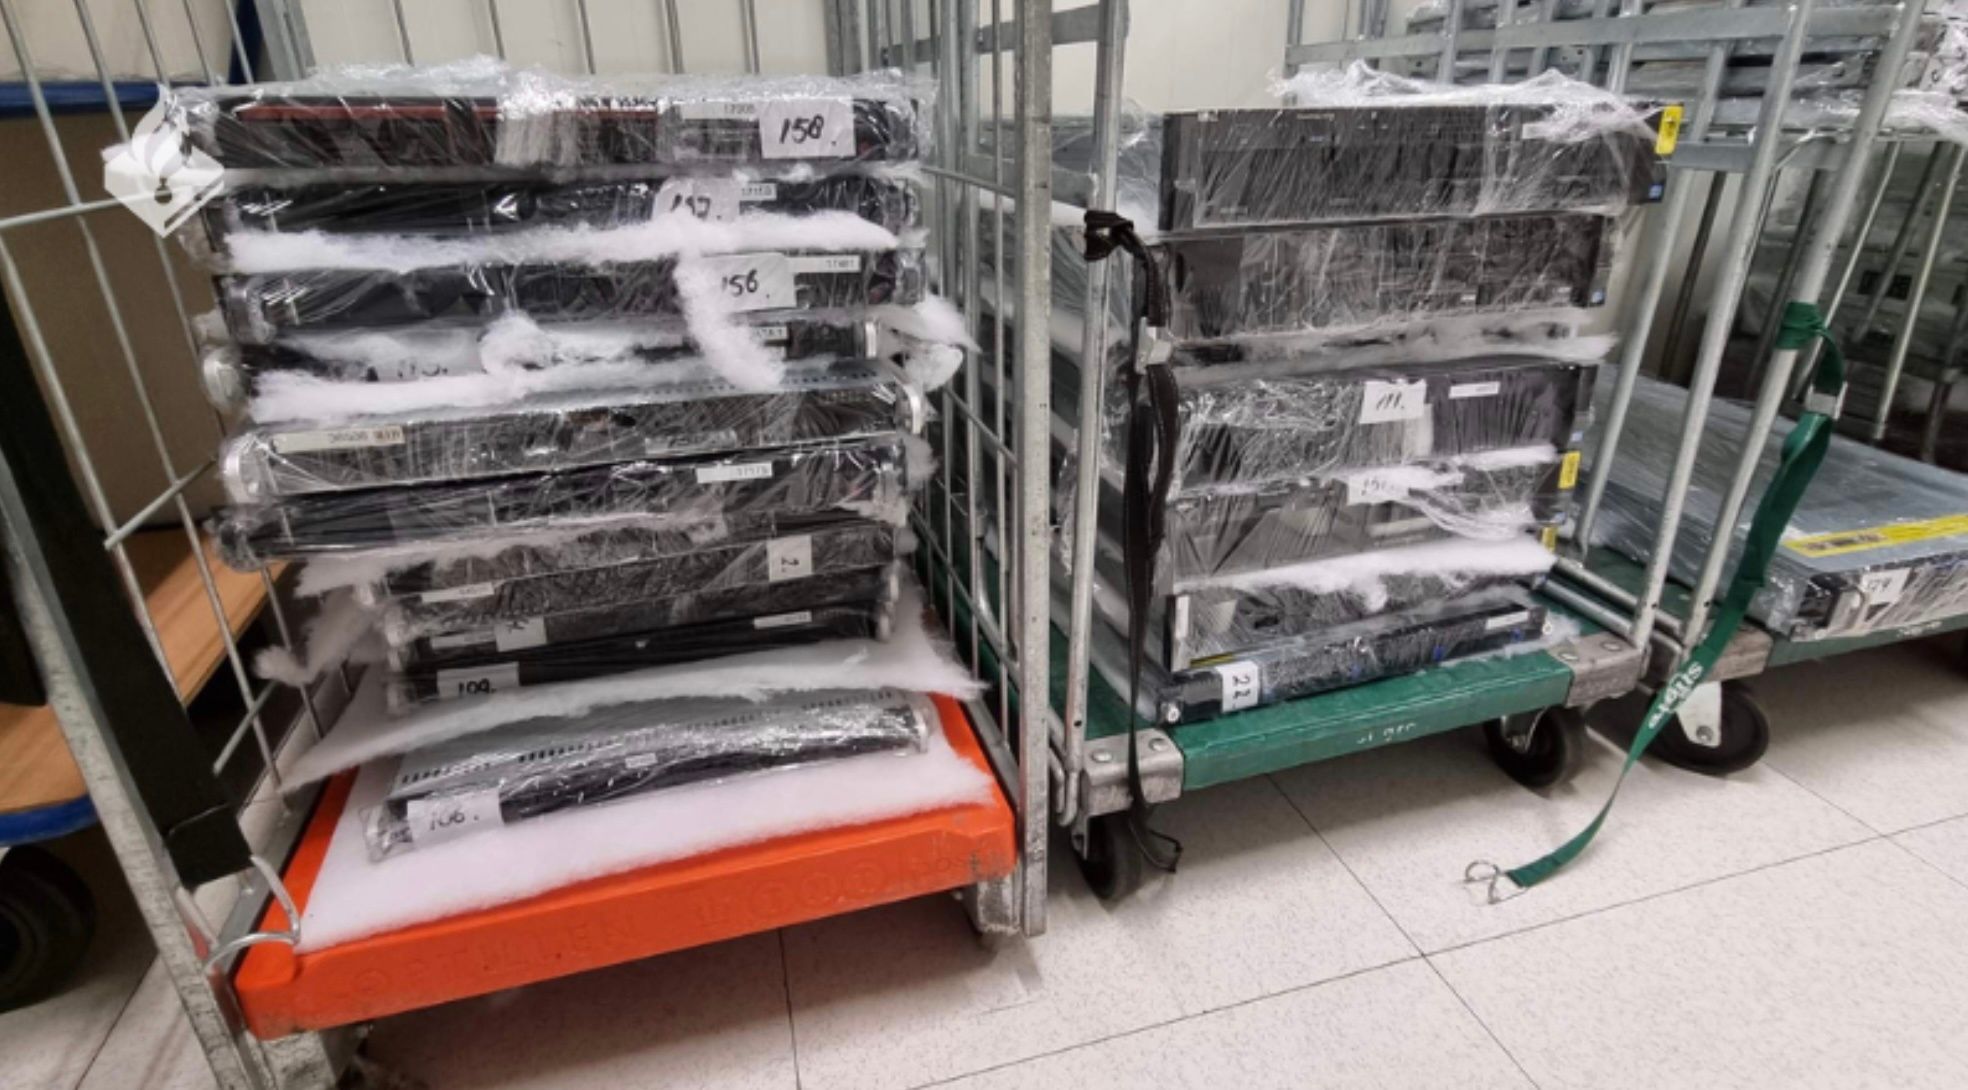
Dutch National Police, coordinating with international partners, seized and took offline 127 servers associated with ZServers/XHost at the Paul van Vlissingenstraat colocation facility in Amsterdam. The operation followed over a year of investigation and occurred within 24-48 hours of the joint sanctions announcement on February 11, 2025. This action effectively dismantled ZServers/XHost's major Western-facing infrastructure. [2][5]
ASD Offensive Cyber Action (Undated)
Credible Australia's Signals Directorate (ASD) deleted approximately 520 GB of data stolen from Medibank Private in the October 2022 attack from ZServers infrastructure. ASD Director-General Abigail Bradshaw publicly described this and stated ASD has deleted up to 250 TB of stolen data from adversary systems globally. Exact timing of the ZServers-specific action not publicly stated. [1]
Sanctions Actions
| Authority | Date | Action | Legal Basis |
|---|---|---|---|
| OFAC (US) | Feb 11, 2025 | Added ZServers, Mishin, Bolshakov, and 4 crypto addresses to SDN list | EO 13694 / CYBER3; materially assisted LockBit ransomware |
| UK FCDO | Feb 11, 2025 | Asset freeze: ZServers, XHOST Internet Solutions LP, and 6 individuals | UK Cyber Sanctions Regime; LockBit attacks against UK organizations including hospitals |
| AU DFAT | Feb 11, 2025 | Designated ZServers and 5 individuals; first Australian sanctions against a hosting entity; first Australian cyber sanctions related to network infrastructure | Australian autonomous cyber sanctions framework; BianLian hosting; Medibank stolen data hosting |
Post-Disruption Client Migration
Credible Vendor commentary (Intel 471, Arete, TRM Labs) confirms the sanctions and takedown forced LockBit affiliates and other clients to seek alternative infrastructure. Significant substitution capacity exists in the broader BPH ecosystem. [1][7]
Analyst Inference One Exploit forum actor predicted ZServers would rebrand; another characterized it as "a typical resource seller" that could be taken down by a higher-level data center at any time. Named successor providers and documented migration paths are an intelligence gap.
In July 2025, OFAC sanctioned Aeza Group (St. Petersburg, Russia), a separate BPH provider with partial client overlap (BianLian), confirming the ecosystem continued operating via alternative providers after ZServers' disruption. No public connection between Aeza Group and ZServers/XHost has been established.
Connected Groups and Ecosystem Relationships
Each entity carries two independent confidence assessments: Tier 1 (infrastructure relationship) and Tier 2 (operational relationship). These are analytically distinct claims requiring separate evidence bases and are never collapsed into a single label.
Tier 2: OFAC confirms Mishin marketed ZServers to ransomware actors "with the understanding that they would use those services in their cybercriminal activities." The 2023 IP reassignment episode demonstrates active facilitation of the LockBit client against an abuse complainant. However, no public evidence establishes joint operational planning beyond hosting and financial services.
Tier 2: No public evidence ZServers operators were involved in Conti operational planning beyond providing hosting services.
Tier 2: No evidence of operational coordination beyond hosting.
Tier 2: No evidence of operational coordination beyond hosting relationship.
Tier 2: On-chain payment establishes financial relationship only, not operational coordination.
Tier 2: Financial connection only.
Tier 2: The DEDBROPRO profile records "James Pippin" (JP12547-RIPE) as technical contact on AS59753 and as a documented Mishin alias; that person object no longer exists in RIPE (29 Oct 2026) and the alias claim was not re-verified here, so it stands as single-source. Intel 471 named Vault Dweller OU as sharing the XHOST abuse contact. Vault Dweller's registered RIPE contact is a persona, "Alexander P. Frei" (APF32-RIPE, created 2014, Latvian mobile number), and the Estonian register names Yehor Minin as director; neither is a sanctioned ZServers individual. Whether Vault Dweller OU is a ZServers front, a successor vehicle for the same operators, or an independent LIR that sold XHOST its ASN and address space is not resolved. Treat as Credible shared operation pending a named-individual link. Reconstitution relevance: Vault Dweller registered 9 IPv4 blocks between Dec 2025 and Jul 2026, after the ZServers sanctions and while AS197414 went dark (see DEDBROPRO profile, Section 04).
Trajectory Assessment
Historical Market Position
ZServers/XHost occupied a significant structural position in the Russia/CIS-linked ransomware ecosystem for approximately 15 years, serving as a preferred BPH provider for high-end ransomware operations. OFAC and UK FCDO descriptions as "a key component of Russia's cybercrime supply chain" and "the launchpad for crippling ransomware attacks" reflect its prominence by 2023-2024. The September 2024 data breach offering 9,500 client records for sale indicates a substantial historical client base, though active clients at seizure time would be a subset.
Disruption History and Timeline
Trajectory Direction
Disrupted, Reconstitution Risk: Elevated. The February 2025 actions destroyed Western-hosted infrastructure and imposed financial/legal constraints. As of 29 October 2026 every ZServers/XHOST ASN is gone from RIPE and the routing table (AS197414 last seen 4 Dec 2025; AS59753 last seen Nov 2022; the AS200730 successor on the old prefix last seen 26 Jul 2026). The brand itself has not reappeared. The reconstitution signal that does exist runs through Vault Dweller OU (Estonia): the registrant of the ex-XHOST ASN and of the last XHOST-announced prefix added nine IPv4 blocks between December 2025 and July 2026 and operates the DEDBROPRO brand (see Section 09). Earlier indicators: website online as of March 2025, ASN still registered, forum commentary anticipated rebrand. Given the pattern of Russia-based BPH providers reconstituting under new names (see: Aeza Group, sanctioned July 2025, operating concurrently and separately), the probability of Mishin or associates reconstituting a BPH operation under a new brand in Russian or permissive-jurisdiction hosting is assessed as elevated, though unconfirmed as of mid-2026.
Intelligence Gaps
Partially closed. AS200730 is gone (unrouted 26 Jul 2026, no RIPE object) and 87.251.64.0/24 is an individual assignment under a Russian LIR with no operator link. The live question is Vault Dweller OU (Estonia), which held AS59753 XHOSTIS-AS, still owns 185.170.144.0/24, shares Hostkey, and kept registering address space after the sanctions. Close with: Estonian business register filings for reg-nr 14752442 (director, beneficial owner, filing history); InterLIR lessee records; a named-individual link between Vault Dweller contacts and the six designated ZServers persons.
Whether ZServers reconstituted post-February 2025 under a new brand, legal entity, or new ASN beyond the documented IP space reallocation. Close with: longitudinal C2/infrastructure tracking; criminal forum monitoring for new BPH ads by triplex560-linked personas.
Whether ZServers held additional ASNs or IP allocations. Close with: RIPE/ARIN historical data; Spamhaus SBL records correlated to entity; vendor infrastructure mapping.
Upstream transit providers beyond confirmed Hostkey. Close with: BGP historical analysis; network operator community posts; additional breach material.
First-listing dates, delisting events, specific SBL entry numbers. Close with: direct Spamhaus/abuse.ch dataset queries against documented IP ranges; vendor correlation.
9,500 client records not publicly enumerated, specific named clients and their criminal operations. Close with: law enforcement analysis of the breach; vendor processing of the leaked dataset.
Technical responsibilities of Sidorov, Dmitriy Bolshakov, Odintsov, and Ananev. Close with: full UK FCDO and AU DFAT sanctions notices; law enforcement evidence.
Which specific BPH providers absorbed LockBit and other clients post-February 2025. Close with: longitudinal C2/leak-site infrastructure tracking; vendor reports on successor infrastructure.
Whether US DOJ or allied prosecutors filed sealed charges against operators. Close with: public disclosure upon arrest; non-sealed docket records.
Any direct tasking, protection, or coordination with Russian security services. Close with: court documents, leaked communications, or declassified intelligence.
Concrete ZServers-hosted IPs and domains used in documented LockBit, Conti, or BianLian campaigns. Close with: law enforcement technical annexes; vendor IoC feeds with explicit ZServers attribution.
Post-Disruption Developments (February 2025 to October 2026)
87.251.64.0/24 by AS200730 (holder: ISAEV ISAEV Igor, WHOIS empty); 185.170.144.0/24 by AS50053 (VDSKA-AS, Anton Levin). No confirmed ZServers rebrand or successor entity. ZServers remains on OFAC SDN, UK FCDO, and AU DFAT sanctions lists.