Executive Summary and Provider Overview
Unlike sanctioned peers (Aeza, ZServers), no individual operator, administrator, or handle has been publicly and specifically attributed to Virtualine. No Virtualine principal has been named, indicted, or sanctioned by any authority, and the 27 October 2026 domain seizure announcement named no operator and announced no charges. Per the operator-profiles rule, no escalated hero module is presented; the absence of a named operator is itself a material finding and is documented as a primary intelligence gap (see Sections 02 and 10). [2][3][9]
Quick-Reference Attributes
| Common Names | Virtualine; Virtualine Technologies; virtualine.net / virtualine.org; associated brands Railnet (RAILNET), OMEGATECH-AS; aliases cited by DOJ and Chainalysis: Secury, Massgod, Spamhouse, Lanedo, Omegatech [17][18] |
|---|---|
| Node Type | Bulletproof Hosting Provider (rotating shell-company / ASN cluster) |
| Status | Disrupted - primary domain virtualine.net seized by the FBI on 27 October 2026 (Operation Omegaline, EDVA). Backbone AS214943 (Railnet) has announced no prefixes since 12 February 2026 and its RIPE registration has been deleted; OMEGATECH (AS202412) is visible to a single route collector peer as of 29 October 2026. AS209800 remains routed. The operator stated on virtualine.org and Telegram that it can rebrand and continue; no arrests or charges announced. [14][15][17][19] |
| Entity Registration Jurisdiction | Split / obfuscated. Backbone front Railnet LLC registered in Kentucky, US (registered agent White Label Networks LLC, Israel). OMEGATECH front associated with Seychelles. The "Virtualine Technologies" brand itself has no confirmed single legal registration in open reporting; assessed Russia-linked. AS209800 was registered by fraudulently impersonating a legitimate German company (metaspinner net GmbH). [3][5][4] |
| Infrastructure Hosting Jurisdiction | Primary European footprint routed through Germany (aurologic GmbH, Langen; secondary Pfcloud UG). ASN registrations span RIPE region (Seychelles/GB/UK country codes). No confirmed self-operated Russian datacenter documented. [2][3] |
| Assessed Operator Location | Russia (assessed). Virtualine is described across vendor reporting as a "Russia-based" / "Russia-linked" provider advertised on Russian-language forums; specific operator identity and physical location are unknown. [2][5] |
| Active Period | Tracked by Intrinsec across at least three reports, March 2025 to June 2026; Railnet ASN (AS214943) and Virtualine brand observed from early 2025; Exploit forum account from 28 August 2024; storefront domain seized 27 October 2026. [1][2][16] |
| Primary ASNs | AS214943 (RAILNET, backbone; unrouted since Feb 2026, RIPE object deleted); AS202412 (OMEGATECH-AS; near-zero routing visibility Oct 2026); AS215789, AS214940 (Virtualine-linked); AS209800 (metaspinner impersonation; still routed Oct 2026). [2][3][7][19] |
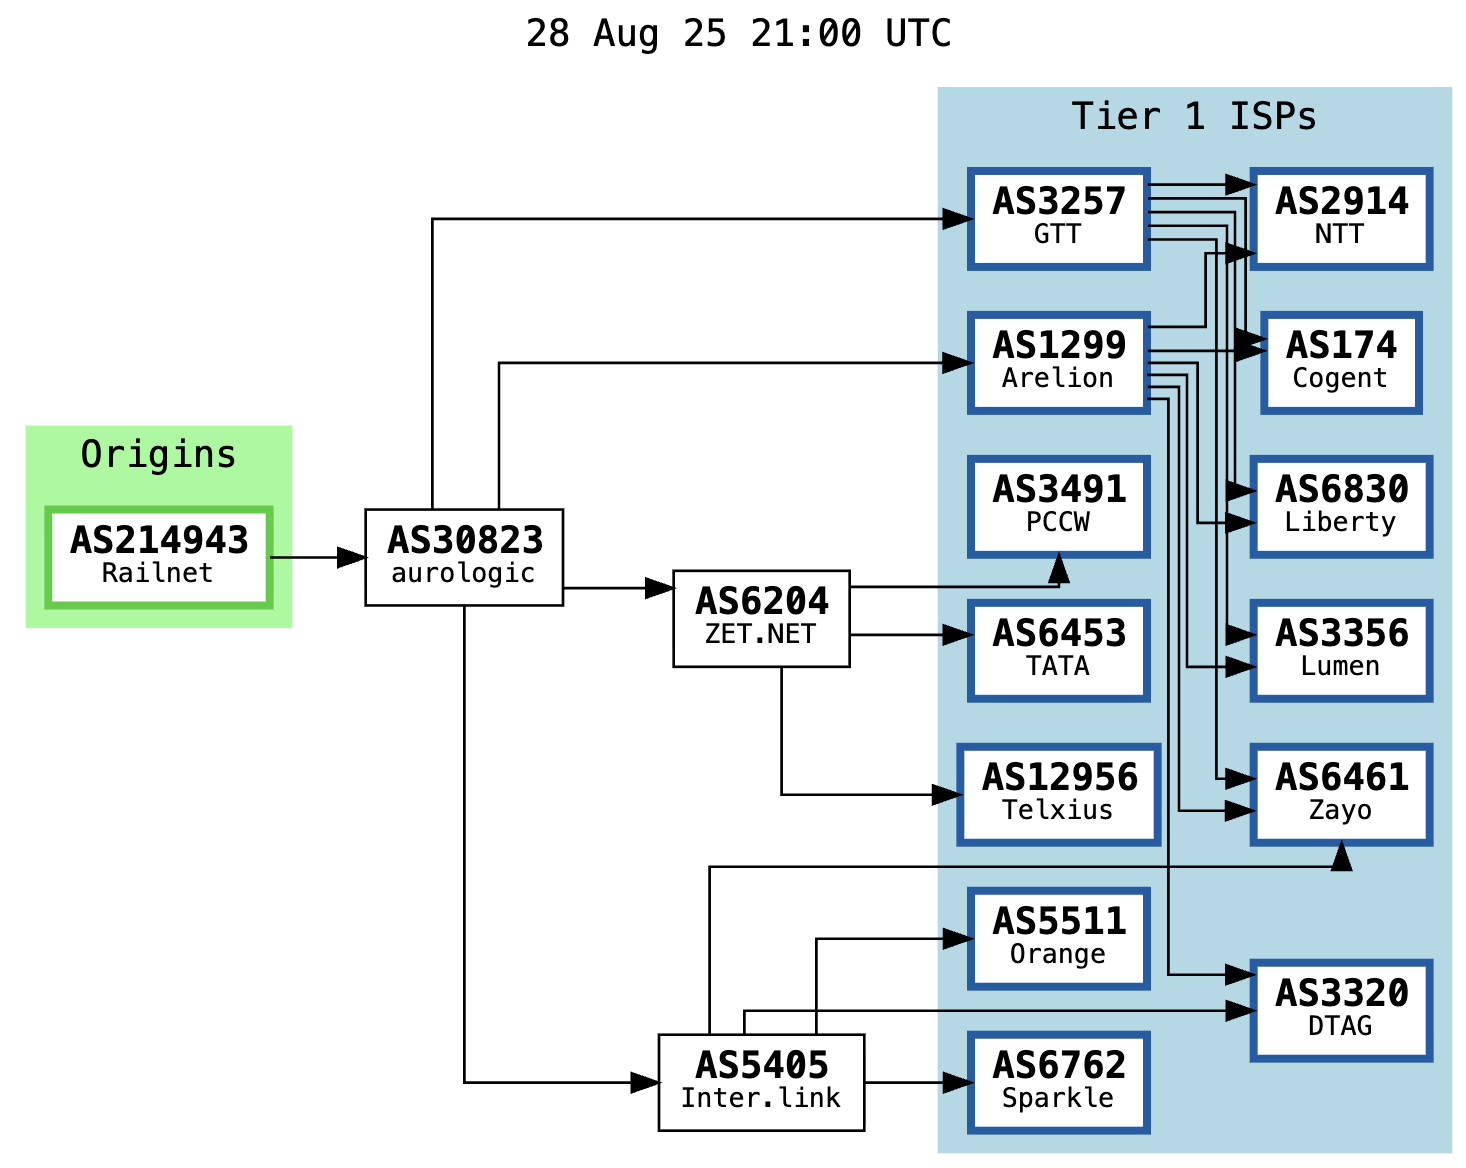
| Upstream Transit | AS30823 aurologic GmbH (Germany, primary upstream, ~95% of Railnet traffic); AS51396 Pfcloud UG (Germany, secondary). [3] |
| Abuse Posture | Verbatim self-marketing: "DMCA & Abuse Ignored"; "Пуленепробиваемый" (bulletproof). Support via 24/7 web ticket portal and Telegram bot @virtualine_bot. [Perplexity/forum ad] |
| Sanctions | NOT SANCTIONED No OFAC SDN, EU, UK, or Australian designation identified against Virtualine, Railnet LLC, White Label Networks LLC, or OMEGATECH as of 29 October 2026. The 27 October 2026 action was a domain seizure, not a designation. [9][10][14] |
| Blocklist Standing | Spamhaus ASN-DROP: RAILNET (AS214943) LISTED ("under control of cyber-criminals"); OMEGATECH (AS202412) flagged by Spamhaus as a Virtualine front; abuse.ch ThreatFox IOC-level entries on OMEGATECH IPs. [2][3][4] |
| State Nexus Tier | No confirmed state nexus (Tier: NONE) - with a client-side caveat (hosted UAC-0050, assessed by CERT-UA as Russian-law-enforcement-linked). [1] |
Overall Assessment
Virtualine (Virtualine Technologies) is a Russia-linked bulletproof hosting cluster that advertises openly on Russian-language underground forums as abuse-tolerant "offshore" hosting while presenting a legitimate-looking retail storefront at virtualine.net. Rather than a single stable legal entity, it operates as a rotating set of shell-company fronts and autonomous-system brands, principally the Railnet LLC backbone (AS214943, Kentucky-registered) plus OMEGATECH (AS202412) and, most recently, AS209800, an autonomous system registered by fraudulently impersonating a legitimate German software company. Spamhaus attributes OMEGATECH directly as "just another network created by hosting provider Virtualine," and Recorded Future / Insikt Group lists Virtualine Technologies among the threat activity enablers dependent on German upstream aurologic GmbH. [2][3][4]
The operating model is classic BPH: legitimate-looking retail hosting UI paired with explicit "DMCA & Abuse Ignored" advertising to criminal buyers, low-friction unvetted onboarding, persistent Spamhaus ASN-DROP listing, and rapid ASN/prefix churn to evade blocklisting. The cluster hosts a broad crimeware portfolio: ransomware C2 (Lynx), malspam and JS-backdoor campaigns (BEC/EAC), multi-family RAT and botnet C2 (one OMEGATECH subnet observed hosting 67 C2 servers across 16 malware families), a DDoS/loader botnet (Kamasers), and phishing. [2][8]
Virtualine is assessed as Disrupted as of 27 October 2026. The FBI Washington Field Office and the US Attorney for the Eastern District of Virginia seized virtualine.net under Operation Omegaline, with Polizei Hessen, Politie Midden-Nederland, the UK NCA and private partners OverRIPE and Lumen. The seizure followed a routing collapse already visible in BGP: Railnet (AS214943) stopped announcing on 12 February 2026 and OMEGATECH (AS202412) had fallen to a single visible peer by late October 2026; only AS209800 remains routed. Prosecutors allege the service accepted bitcoin to unhosted addresses under a "BTC [NO-AML]" label, laundered proceeds, and knowingly kept a forum selling sexual images of minors online after warnings in January 2026 from German, Canadian and Australian authorities and NCMEC. No operator was named and no charges were announced. As of the May 2026 Intrinsec reporting, OMEGATECH had generated 642,001 honeypot hits in March 2026 alone and continued to host live malware C2, and the Monero-branded VPS product line remained on sale at virtualine.net. [14][15][17][18][19] The two defining analytical features are (1) a genuinely traceable US/Israel corporate front (Railnet LLC in Kentucky, registered agent White Label Networks LLC), which is the strongest structural leverage point, and (2) the complete absence of any named operator or any sanctions designation, in sharp contrast to sanctioned peers Aeza and ZServers. The single largest external dependency is the German upstream aurologic GmbH, which carries roughly 95% of Railnet traffic. [2][3]

Lineage and Organizational Heritage
Corporate Structure and Shell Layering
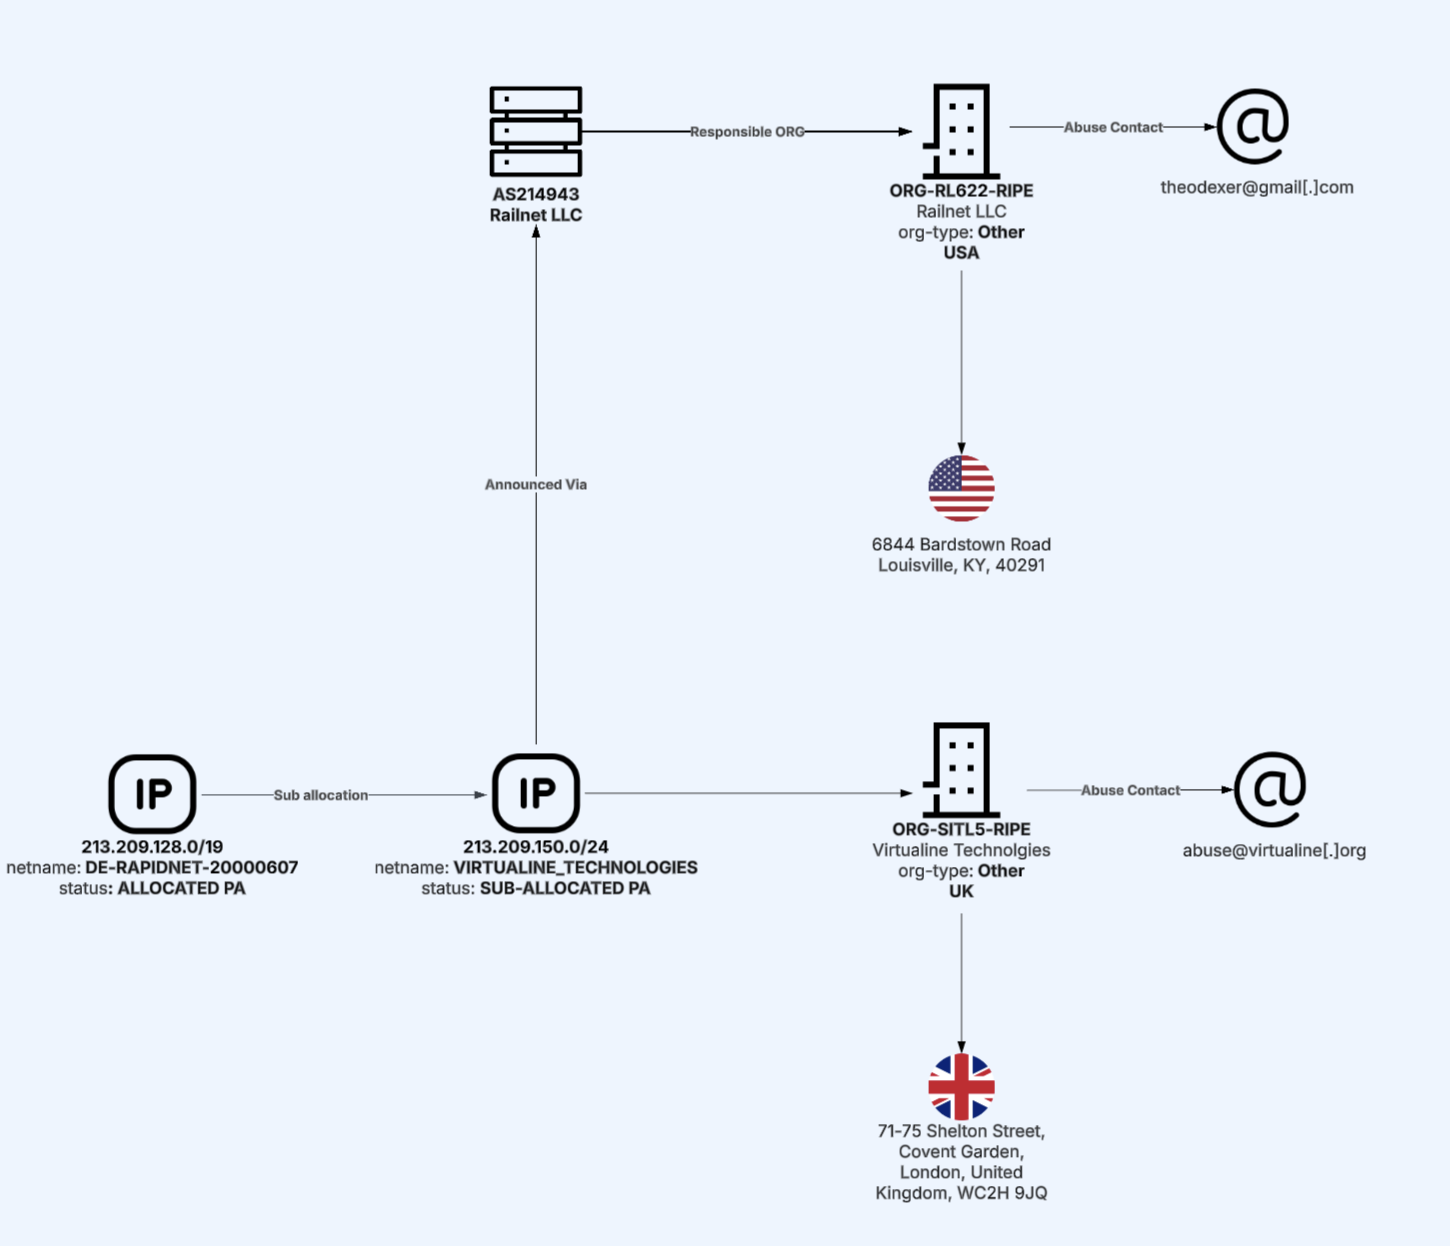
Virtualine's most consistently documented legal front is Railnet LLC, a shell company registered in Kentucky, United States. Railnet LLC's registered agent is White Label Networks LLC, an Israeli company that Intrinsec identifies as "known for its links with illicit hosting networks." This produces a concrete, named US-jurisdiction pressure point: a Kentucky LLC (subject to Secretary of State disclosure and process-service requirements) fronted by an Israeli-registered agent, both named explicitly in primary reporting rather than assessed by inference. [1][2]
Recorded Future / Insikt Group provides the clearest structural picture: Railnet LLC is the backbone that originates the prefixes, and the "Virtualine Technologies" brand appears as a downstream sub-allocation (from Rapidnet) routed through Railnet. Insikt Group lists Virtualine Technologies among the threat activity enablers (TAEs) dependent on aurologic GmbH, alongside Femo IT Solutions, Global-Data System IT Corporation, and the sanctioned Aeza Group. [3]
Confirmed Railnet LLC (AS214943) is the operational backbone. RIPE sub-allocation records (via Recorded Future) show Virtualine Technologies, and additional downstream brands DripHosting and RetryHost, receiving IP space routed through Railnet LLC. Spamhaus independently attributes OMEGATECH (AS202412) as "just another network created by hosting provider Virtualine." [3][2]
Brand, Entity, and Sibling Structure
| Entity / Brand / ASN | Jurisdiction / Identifier | Role | Active Window (Observed) | Confidence |
|---|---|---|---|---|
| Railnet LLC (RAILNET, AS214943) | Kentucky, US (LLC); UK country code in some ASN records | Backbone entity; originates prefixes; Spamhaus ASN-DROP listed | Early 2025 - present | Confirmed |
| White Label Networks LLC | Israel | Registered agent for Railnet LLC; "known for links with illicit hosting networks" | Observed 2025-2026 | Confirmed |
| Virtualine Technologies (AS215789, AS214940) | Assessed Russia-linked; sub-allocated from Rapidnet, routed via Railnet | Core brand; hosted UAC-0050/UAC-0006 spam infrastructure | 2025 - present | Confirmed |
| OMEGATECH-AS (AS202412) | Seychelles (RIPE region); domain virtualine.org | Front network; hosted JS-backdoor and multi-family C2 | ~Jan 2026 - present | Confirmed |
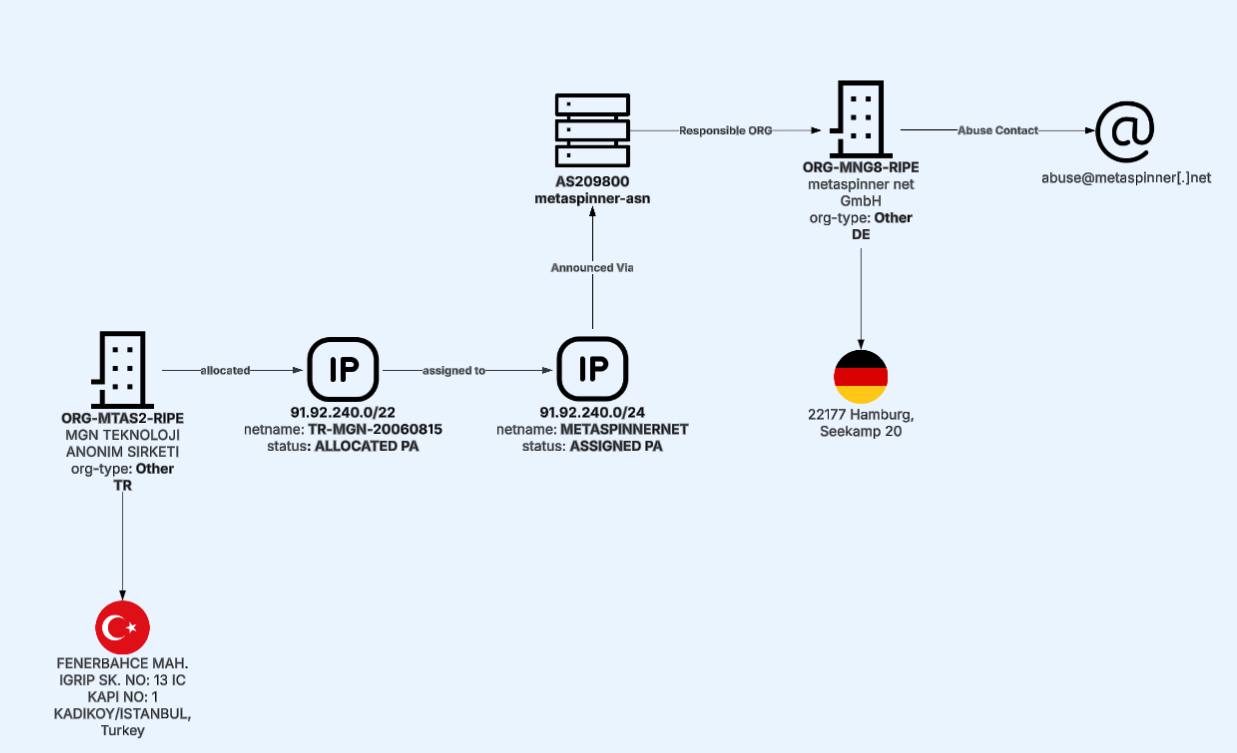
| AS209800 ("metaspinner") | Registered by fraudulent impersonation of metaspinner net GmbH (Hamburg, DE) | Newly acquired front; heavy malware footprint; routed via aurologic | Created Apr 25, 2025; expansion reported Sep-Nov 2025 | Confirmed |
| DripHosting; RetryHost | Sub-allocated from Euro Crypt EOOD / Telco Power Ltd, routed via Railnet | Downstream reseller/sub-brands on Railnet backbone | 2025 (RIPE-observed) | Credible |
| GHOSTYNETWORKS (AS205759) | Kentucky, US | Sibling BPH network co-hosting the same malspam; assessed OPTIBOUNCE/AnonRDP rebrand, NOT confirmed Virtualine-owned | Allocated Jan 2026 - mid-2026 | Credible (distinct) |
| FDN3 (AS211736) cluster | Ukraine / Seychelles | Inherited Virtualine prefix 88.210.63.0/24 (Jun 2025); linked to Global Connectivity Solutions LLP / Zservers ecosystem | ASN created Aug 2021; prefix moved Jun 2025 | Credible (distinct) |
Reporting frequently discusses three related-but-distinct BPH entities together because they co-host the same malspam campaigns and share German upstreams: (1) Virtualine / Railnet / OMEGATECH; (2) GHOSTYNETWORKS / OPTIBOUNCE / AnonRDP; and (3) the FDN3 / Ukrainian-Seychelles cluster linked to Global Connectivity Solutions LLP and Zservers. Intrinsec treats these as separate operations with only infrastructural/upstream overlap, not shared ownership. Analysts should not merge them despite their consistent joint appearance. [2][3]
Evidence Basis for Lineage Claims
| Evidence Type | Finding | Confidence |
|---|---|---|
| Infrastructure continuity | Virtualine Technologies sub-allocation (from Rapidnet) routed through Railnet LLC; RIPE-documented | Confirmed |
| Infrastructure continuity | OMEGATECH (AS202412) attributed by Spamhaus as "just another front of Virtualine"; domain virtualine.org tied to the ASN | Confirmed |
| Infrastructure continuity | Prefix 88.210.63.0/24 moved from Virtualine (AS214940/AS214943) to FDN3 (AS211736), June 2025 | Credible |
| Corporate / legal continuity | Railnet LLC (Kentucky) to White Label Networks LLC (Israel) registered-agent chain, across multiple Intrinsec reports | Confirmed |
| Personnel / handle continuity | No named individual operator publicly attributed to Virtualine | Gap - not established |
| Upstream continuity | Shared aurologic (AS30823) / Pfcloud (AS51396) upstream pairing across cluster; ~95% of Railnet traffic via aurologic | Confirmed |
Operator Profiles (Mandatory Subsection)
No individual operator, administrator, or handle has been publicly and specifically attributed to Virtualine itself in available reporting. This is a significant intelligence gap, flagged rather than inferred:
- Railnet LLC / White Label Networks LLC: No named principal, officer, or beneficial owner publicly disclosed in sourced reporting. Nationality/location of the controlling operator is unknown. Legal status: not sanctioned, not indicted, not publicly named as an individual defendant. Railnet LLC has not appeared on the OFAC SDN list per available search tooling. [9][10]
- Adjacent (distinct) network for contrast: The GHOSTYNETWORKS / OPTIBOUNCE network's registered organizer, Daniel Mishayev, is named across Kentucky business filings tied to Spamhaus-blocked ASNs; an upstream (SMARTNET LIMITED) reportedly stated Mishayev "only provides the ASN and company registration" and is "not involved in everyday operations." This individual is not confirmed connected to Virtualine/Railnet; the two are parallel BPH operations that share upstreams and appear in the same campaigns. [2]
Kentucky's registered-agent structure means Railnet LLC's filings and registered agent are publicly searchable through the Kentucky Secretary of State's online business database. This is the same public-records mechanism used to identify the organizer behind the separate GHOSTYNETWORKS/OPTIBOUNCE network, underscoring that these Kentucky shell registrations are traceable even when underlying operators are offshore. [2]
Operational and Business Model
Service Model
Virtualine markets itself as abuse-tolerant, general-purpose "offshore hosting" rather than positioning narrowly as crimeware-specific. The public storefront (virtualine.net) advertises standard consumer hosting (cPanel, LiteSpeed, Softaculous, Imunify360, SSL) alongside its bulletproof/DMCA-ignored offshore tier. This dual-branding, a legitimate-looking retail UI paired with explicit "abuse ignored" advertising on criminal forums, is the standard BPH pattern for maintaining plausible deniability with upstream and payment partners while marketing openly to criminal buyers on Russian-language forums (XSS, Exploit, nohide.space). [2]
Verbatim Advertising Copy
Russian copy: "Оффшорный веб-хостинг от $0.79 ★ Оффшорные локации, ★ Пуленепробиваемый, ★ NVMe SSD" (translation: "Offshore web hosting from $0.79, offshore locations, bulletproof, NVMe SSD").
Support: 24/7 web ticket portal and Telegram bot @virtualine_bot.
Unlike Aeza (which relied on resellers to use the word "bulletproof"), Virtualine markets the term directly. The Russian "Пуленепробиваемый" (bulletproof) and English "DMCA & Abuse Ignored" are used as primary self-description in dated, sourced forum advertising.
Pricing (Documented Examples)
| Tier | Config | Price |
|---|---|---|
| Bulletproof VPS (Windows/Linux/MacOS) | entry tier | from $4.99/mo |
| cPanel offshore hosting | entry tier | from $0.79/mo |
| Monero Cloud VPS Standard #1 | 2 GB RAM / 30 GB NVMe | $7.49/mo |
| Monero Cloud VPS Storage Optimized #8 | 64 GB RAM / 1 TB NVMe | $189.99/mo |
| Additional IPv4 | per address | $1 each |
Onboarding
Public self-service signup through virtualine.net combined with a 24/7 Telegram bot (@virtualine_bot) for support: a low-friction, largely unvetted (no-KYC) onboarding model typical of BPH providers seeking volume over selectivity. [2]
Reseller / Downstream Chain
Credible Recorded Future RIPE evidence shows the Railnet backbone routing multiple downstream sub-brands beyond the core Virtualine brand, including DripHosting (sub-allocated from Euro Crypt EOOD) and RetryHost (from Telco Power Ltd). This indicates Railnet functions as a multi-brand backbone reselling IP space to several downstream hosting fronts, not a single storefront. The full identity and scale of the downstream reseller network remain incompletely documented. [3]
Abuse-Handling and OPSEC Posture
The verbatim "DMCA & Abuse Ignored" claim, combined with sustained Spamhaus SBL/ASN-DROP listings across every Virtualine-linked ASN and the practice of acquiring new prefixes through Turkey- and US-based IP brokers with poor vetting (and, in the AS209800 case, outright fraudulent AS registration), indicates a deliberate non-response-to-abuse policy and an evasion-first OPSEC model. Upstream providers aurologic GmbH and Pfcloud UG have been separately documented (Recorded Future) as tolerating abusive downstream customers, effectively shielding Virtualine/OMEGATECH from upstream-level abuse enforcement. [2][3][4]
Technical Capabilities and Infrastructure Footprint
ASN Details
| ASN | Name | Registration Country | Notes |
|---|---|---|---|
AS214943 | RAILNET | US (Kentucky LLC); UK country code in some ASN records | Backbone; Spamhaus ASN-DROP "Blocked - under control of cyber-criminals"; ~19 prefixes (Aug 2025), ~95% via aurologic. RIPEstat: zero prefixes announced since 12 February 2026; no aut-num object in the RIPE database as of 29 October 2026 (deletion date not exposed). Silent Push observed infrastructure moving off Railnet to OMEGATECH on 11 February 2026. [15][19] |
AS214940 | Virtualine-linked | US-attributed | Prefix 88.210.63.0/24 later inherited by FDN3 |
AS215789 | Virtualine | Assessed Russia-linked | Hosted UAC-0050 spam infrastructure, 2025 |
AS202412 | OMEGATECH-AS | Seychelles (RIPE region); domain virtualine.org | 9 IPv4 CIDR blocks incl. 45.132.180.0/24, 91.92.240.0/22, 94.26.38.0/24, 94.154.35.0/24, 130.12.180.0/24, 146.19.125.0/24, 158.94.208.0/22, 178.16.52.0/22, 193.30.241.0/24. RIPE: aut-num created 12 January 2026 under maintainer omegatechsc-mnt (org ORG-OL329-RIPE), which also holds 146.19.125.0/24 and 45.132.180.0/24 (both registered April and October 2024). RIPEstat 29 October 2026: visible to one route collector peer, last seen 27 October 2026. Silent Push: disrupted but not fully offline. [15][19] |
AS209800 | "metaspinner" (fraudulent) | Impersonated metaspinner net GmbH (Hamburg, DE) | Created Apr 25, 2025; announced exclusively via aurologic; heavy malware footprint (SmokeLoader, TinyLoader, Stealc, Amadey, Cobalt Strike, Moobot); later re-described as "LANEDONET". RIPE: maintained by SBMT (Securebit AG, a Swiss sponsoring LIR with 700+ objects), so the maintainer footprint does not isolate Virtualine. RIPEstat 29 October 2026: still announcing (1 IPv4, 1 IPv6 prefix), the only Virtualine-linked ASN with normal visibility after the seizure. [19] |
Upstream Transit and Provider Chain
Confirmed Virtualine's cluster depends on two German upstreams: aurologic GmbH (AS30823) and Pfcloud UG (AS51396). Recorded Future's August 2025 BGP snapshot shows Railnet originating nineteen IPv4 prefixes with roughly 95% routed via aurologic and a single /24 via Pfcloud UG. aurologic (formed 2023 from Combahton GmbH's fastpipe.io network, operating from Tornado Datacenter GmbH in Langen, Germany) is documented by Recorded Future / Insikt Group as a central enabler for multiple Russia-linked BPH networks, including the sanctioned Aeza Group, Femo IT Solutions, Global-Data System, and Railnet itself. [3]
No upstream de-peering event specific to Virtualine, Railnet, or OMEGATECH has been documented in available sources. Railnet's withdrawal from the routing table on 12 February 2026 and OMEGATECH's collapse to one visible peer in October 2026 are observed in BGP data, but no source attributes either to an upstream cutting service rather than to the operator moving or abandoning the ASNs. [15][19] aurologic continued to provide connectivity to Railnet and to the fraudulently registered AS209800 through at least late 2025, and continued serving the US/UK-sanctioned Aeza International over the same period, indicating no de-peering has yet occurred against Virtualine-linked networks through this upstream. This is a key structural observation: the German upstream remains the un-actioned chokepoint. [3]
Resilience Techniques
The cluster exhibits classic BPH resilience: rapid ASN churn (Virtualine to OMEGATECH to AS209800 fronts), prefix hopping between related networks (88.210.63.0/24 moved to FDN3, June 2025), acquisition of fresh IPv4 space through poorly-vetting Turkey- and US-based IP brokers, fraudulent AS-level impersonation of a legitimate company (metaspinner), and reliance on abuse-tolerant German upstreams to maintain connectivity despite persistent blocklisting. [2][3][4]
Hosted Activity Types
| Category | Evidence Basis | Confidence |
|---|---|---|
| Ransomware C2 (Lynx) | DFIR Report / Intrinsec attribute a specific IP to Railnet LLC/Virtualine in a Lynx case (195.211.190[.]189) | Credible (IP not re-verified this pass) |
| Ransomware initial access (Black Basta, Cactus, RansomHub) | Attributed via related Global Connectivity Solutions LLP / Railnet ecosystem enabling brute-force initial access | Credible |
| Malspam / JS-backdoor C2 (BEC/EAC) | Intrinsec May 2026 report; OMEGATECH hosting C2 (e.g., 91.92.243[.]79, 158.94.211[.]76) | Confirmed |
| DCRat / stealer C2 and phishing | abuse.ch ThreatFox entry on OMEGATECH AS202412 (91.92.240[.]117:80); 35+ Apple iCloud/Find My phishing domains | Credible (single tracker) |
| Multi-family botnet/RAT hosting | BreakGlass Intelligence: one OMEGATECH subnet hosting 67 C2 servers across 16 malware families (Remcos, AsyncRAT, Amadey, Latrodectus, XWorm, Stealc, DCRat, LOBSHOT, Mirai, Bashlite, Quasar, ClearFake, SectopRAT, and others) | Credible |
| Child sexual abuse material forum ("Vendor 1") | DOJ (27 Oct 2026): Virtualine allegedly provided an IP to a forum selling sexual images of minors and adults, received warnings in January 2026 from German, Canadian and Australian police, NCMEC and a victim's attorney, kept it online and helped build a successor upload site | Confirmed (prosecutor allegation, court-authorized seizure) |
| DDoS / loader botnet (Kamasers) | C2 on Railnet ASN; April 2026; Latrodectus (TA577) links; targeting CH, DE, UA, PL, FR | Credible |
| SSL VPN/RDP brute-force initial access | Via inherited prefix 88.210.63.0/24 (Virtualine to FDN3); peak July 6-8, 2025 | Credible |
Blocklist Standing
| Blocklist | Status | Notes |
|---|---|---|
| Spamhaus SBL / ASN-DROP | LISTED | AS214943 (RAILNET) flagged "Blocked - under control of cyber-criminals"; AS202412 (OMEGATECH) flagged as a Virtualine front; AS209800 reported by Spamhaus as an AS-level impersonation |
| abuse.ch ThreatFox | LISTED (IOC-level) | Direct IOC entries for OMEGATECH IPs, e.g., 91.92.240[.]117:80 (DCRat C2) |
| abuse.ch URLhaus | LISTED | Malware distribution URLs recorded for AS214943 (RAILNET) |
| abuse.ch Feodo Tracker | Not located | No specific Feodo entry tied to Virtualine ranges located this pass |
| Firehol Level 1/2 | Not verified | No direct citation located; verify via direct Firehol dataset query if required |
| Delisting attempts | None documented | Consistent with "abuse ignored" model rather than compliance-seeking behavior |
Known Weaknesses
The most significant documented weakness is the traceable Kentucky/Israel shell-company chain (Railnet LLC / White Label Networks LLC), which gives US and allied researchers a concrete legal entity and jurisdiction to pursue, unlike fully offshore-registered peers. Kentucky's public business-entity search portal makes registered-agent and filing history directly queryable without subpoena. The second is the ~95% dependency on a single German upstream (aurologic), a de-peering chokepoint that has not yet been actioned. The third, newly evident, is that the AS209800 acquisition relied on fraudulent impersonation of a real company (metaspinner net GmbH), which provided that company documentary grounds to disavow the AS and creates a fraud-based enforcement angle. [2][3][4]
Financial Infrastructure
Payment Methods
Virtualine advertises cryptocurrency support and specifically markets a dedicated "Monero Cloud Server" product line "customized for Monero," a privacy coin favored for its non-traceable properties, from $7.49/month. This is an advertised (not inferred) financial feature aimed at the criminal-market segment. [Perplexity/storefront]
Confirmed DOJ (27 October 2026): Virtualine accepted bitcoin through a payment option it labeled "BTC [NO-AML]", directing customers to specific unhosted bitcoin addresses so that payments avoided compliance checks at hosted exchanges, and then laundered the proceeds. [14][17][18]
Wallet Clusters and On-Chain Attribution
Credible Following the seizure, TRM Labs and Chainalysis both published entity-level attribution. TRM labeled Virtualine's bitcoin addresses and reports that in 2026 Virtualine received more illicit-attributed value than any other TRM-labeled BPH provider despite lower total inflows than several peers; direct inflow mix roughly 44% from a Russian drug marketplace, 17% from a sextortion scheme (payments February to June 2026), 13% from a mixer, 5% from ransomware groups, with StealC paying throughout 2026. Chainalysis labeled the addresses in its product suite and reports Reactor exposure to ransomware operators, infostealer infrastructure, Russian-language forums, illicit shops and scam addresses; neither vendor published dollar totals, exchange names or a laundering model. Prior to October 2026 no published on-chain wallet clusters or TRM Labs / Chainalysis / Elliptic entity-specific attributions for Virtualine were located in available reporting. [16][17] No documented three-phase laundering pattern (acquisition / layering / extraction) specific to Virtualine's payment infrastructure has been publicly disclosed. These are material gaps versus the schema's financial-infrastructure requirements and should be pursued with proprietary blockchain-intelligence tooling; open-source reporting does not extend to this level of financial forensic detail for this provider. The Monero-centric product design is itself an intelligence obstacle: it is engineered to defeat exactly the on-chain tracing that produced attributions for BTC/TRON-based peers such as Aeza.
Sanctions and Risk Ratings
NOT SANCTIONED No OFAC SDN, EU Official Journal, UK FCDO, or Australian designation has been identified against Virtualine, Railnet LLC, White Label Networks LLC, or OMEGATECH as of 29 October 2026. The 27 October 2026 FBI action was a court-authorized domain seizure, not a sanctions designation. No VASP-level risk designation was located. The July 13, 2026 US/OFAC action targeting bulletproof/VPN enablers (FirstVPN/1VPNS and associated individuals) did not include Virtualine or Railnet. This unsanctioned status is consistent with the query framing and is a defining contrast with sanctioned peers. [9][10][11]
Client Profile and Hosted Operations
Crimeware Verticals by Evidence Tier
| Client Category | Evidence Basis | Classification |
|---|---|---|
| Ransomware (Lynx) | Direct IP attribution (195.211.190[.]189) to Railnet LLC/Virtualine in a DFIR Report incident writeup | Credible |
| Ransomware initial access (Black Basta, Cactus, RansomHub) | Attributed via associated Global Connectivity Solutions LLP / Railnet ecosystem in Intrinsec 2025 UAC report | Credible |
| Russian-LE-linked mercenary actor (UAC-0050 / "DaVinci Group") | Direct hosting of spam infrastructure on Virtualine AS215789/AS214943; CERT-UA assesses UAC-0050 as linked to Russian law enforcement | Confirmed (hosting) |
| Financially motivated cybercrime (UAC-0006 / SmokeLoader) | Indirect, via related Global Connectivity Solutions LLP infrastructure sharing upstreams with the broader cluster | Credible |
| Botnet/RAT operators (16 malware families on one OMEGATECH subnet) | Direct technical finding (BreakGlass Intelligence) | Credible |
| BEC/EAC malspam operators (JS backdoor) | Direct technical finding (Intrinsec, March-May 2026) | Confirmed |
| CSAM and non-consensual intimate image sellers; hack-for-hire for intimate content | DOJ seizure announcement, 27 October 2026 (forum "Vendor 1") | Confirmed (allegation in court-authorized action) |
| Russian drug marketplace, sextortion scheme, mixers, StealC infostealer, BPH peer Volhav | TRM Labs on-chain counterparties to labeled Virtualine addresses: roughly 44% drug market, 17% sextortion (Feb to Jun 2026), 13% mixers, 5% ransomware groups | Credible (single vendor) |
Client / Target Geography
The March-April 2026 malspam campaigns hosted on OMEGATECH/GHOSTYNETWORKS targeted organizations across CIS and non-CIS states alike (Ukraine, Russia, Poland, Germany, Transnistria), and Intrinsec explicitly flags this as evidence against a CIS-based operator, since CIS-origin actors typically avoid targeting CIS member states. This departs from the classic "CIS exclusion zone" pattern and should be treated as a specific analytical nuance for these particular campaigns rather than a settled attribution of the provider's own location. [2]
Notable Hosted Cases
- Lynx ransomware: Railnet LLC/Virtualine infrastructure (195.211.190[.]189) cited in a DFIR Report incident writeup as the hosting layer for threat-actor infrastructure. Credible (IP not re-verified this pass).
- Kamasers DDoS/loader botnet (April 2026): C2 on a Railnet ASN; loader capability used toward ransomware deployment; Latrodectus (TA577) associations; targeting Switzerland, Germany, Ukraine, Poland, France. Credible.
- TeamPCP supply-chain attacks (LiteLLM PyPI trojanization, March 2026): hosted on the closely associated but distinct GHOSTYNETWORKS (C2 domain litellm[.]cloud), not confirmed as Virtualine directly. Included here only to mark the boundary between the two networks. [2]
State Nexus Assessment
Available reporting does not establish direct evidence of Russian state tasking, coordination, or protection specific to Virtualine. The relationship documented is a commercial hosting-customer dynamic consistent with a tolerated criminal marketplace, not probable operational cooperation or direct control. Overall confidence: MODERATE.
Expected Indicators If Nexus Existed (and Their Absence)
- No sanctions designation citing state-directed activity: Virtualine has no OFAC/EU/UK designation at all, let alone one alleging state tasking (contrast Aeza, sanctioned partly for hosting the Kremlin-directed Social Design Agency).
- No documented law-enforcement immunity specific to Virtualine operators: because no operator is named, no pattern of selective non-enforcement can be attributed to the individual level.
- No direct financial or personnel links to Russian intelligence services appear in the sourced material.
- Behavioral counter-indicator: the March-April 2026 campaigns hosted on the cluster targeted CIS states (including Russia), which is atypical of state-protected Russian actors and argues against a protected-asset reading of at least those campaigns.
Client-Side Caveat (Not Provider-Side Evidence)
Virtualine/Railnet infrastructure hosted spam campaigns for UAC-0050, which CERT-UA assesses with high confidence to be "a mercenary group associated with Russian law enforcement agencies," reportedly operating under an entity called "DaVinci Group" established shortly before the 2022 invasion. This establishes that a Virtualine client has an assessed state-security connection, but it is a statement about the client's affiliations, not evidence that Virtualine itself receives state tasking, protection, or coordination. It is flagged as a data point warranting continued monitoring, not a finding that escalates the provider's tier. [1]
| Nexus Tier | Assessment |
|---|---|
| Direct Control | Rejected - no evidence |
| Probable Cooperation | Rejected - no provider-level tasking/protection evidence |
| Tolerated Safe Harbor | Possible baseline - plausible given assessed Russia location, but not evidenced at operator level (operator unnamed) |
| No Nexus | ASSESSED - best-supported tier at the provider level on current evidence; UAC-0050 client relationship monitored |
Law Enforcement and Regulatory Response
Confirmed On 27 October 2026 First Assistant US Attorney Theophani K. Stamos (Eastern District of Virginia) and FBI Washington Field Office Assistant Director in Charge Darren B. Cox announced the court-authorized seizure of virtualine.net, with Germany's Polizei Hessen, the Netherlands' Politie Midden-Nederland and the UK National Crime Agency, and private partners OverRIPE, Lumen and Chainalysis. Court records describe hosting for "all illegal/black hat activities" (Exploit.in, September 2024), a "BTC [NO-AML]" payment channel to unhosted addresses with subsequent laundering, and the knowing retention of a CSAM forum ("Vendor 1", assigned an IP in about December 2025) after January 2026 warnings; the release states Virtualine still hosts the successor upload site it helped Vendor 1 build. AUSAs Laura D. Withers and Stefanie A. Schwartz represent the government; the DOJ Office of International Affairs assisted. No operator was identified, no arrests or charges were announced, and no sanctions designation was issued; virtualine.org remained online carrying an open letter stating the operator could rebrand and continue. The upstream aurologic GmbH was not named. [14][15][17][18]
Post-Disruption Client Migration
Analyst Inference Too early to measure (two days post-seizure at time of writing). Three indicators to watch: (1) whether AS209800, the only Virtualine-linked ASN still routed, picks up prefixes or C2 that previously sat on OMEGATECH; (2) whether the March 2026 "protection plan" shells surface as new ASNs or sponsoring-LIR allocations; (3) whether virtualine.org and the Telegram channel announce a successor brand, as the operator's open letter promised. Prior to the seizure the observable pattern was offensive-side churn (front rotation and fresh prefix acquisition) driven by blocklisting pressure, not enforcement. [2][3][15]
Connected Groups and Ecosystem Relationships
Each connected-entity claim carries two independent confidence tiers: Tier 1 (infrastructure relationship: did Virtualine/Railnet host or route their infrastructure?) and Tier 2 (operational relationship: did the Virtualine operator know the entity's identity or coordinate operationally?). Given Virtualine's no-KYC, multi-brand-backbone model and its entirely unnamed operator, Tier 2 assessments are inference-level throughout: with no identified operator, operator-level knowledge cannot be evidenced for any client.
Corroborating vendors on the core Virtualine/Railnet/OMEGATECH attribution: Intrinsec, Spamhaus, Recorded Future/Insikt Group, and (secondary) GBHackers/BreakGlass Intelligence. No vendor has published a formal assessment that contradicts the Virtualine-Railnet-OMEGATECH linkage. TRM Labs, Chainalysis, and Elliptic have not published Virtualine-specific on-chain assessments (a financial-attribution gap, Section 05). No named-operator attribution exists from any vendor.
Trajectory Assessment
Infrastructure Churn
Churn is assessed HIGH and deliberate. Within roughly one year the cluster rotated through Virtualine (AS215789/AS214940) to OMEGATECH (AS202412) to the fraudulently registered AS209800, moved prefix 88.210.63.0/24 to FDN3, and continued acquiring fresh IPv4 space through poorly-vetting Turkey- and US-based IP brokers. Through 2025 churn was driven by blocklisting pressure (Spamhaus ASN-DROP) rather than enforcement. In 2026 the pattern inverted: Railnet left the routing table in February and its RIPE object was deleted, OMEGATECH collapsed to one visible peer by late October, and the storefront domain was seized on 27 October. Only AS209800 remains routed. [2][3][4][15][19]
Market Position
Until the October 2026 seizure Virtualine was an active, mid-tier but growing BPH operator with an industrial-scale abuse footprint (642,001 OMEGATECH honeypot hits in March 2026) and a diversified crimeware portfolio (ransomware C2, malspam, multi-family botnet/RAT hosting, DDoS/loader, phishing). Recorded Future's placement of Virtualine Technologies alongside the sanctioned Aeza Group in the aurologic-dependent TAE cohort indicates it is treated by top-tier vendors as a significant node, not a fringe reseller. TRM Labs reports it received more illicit-attributed value in 2026 than any other labeled BPH provider. [2][3][16]
Disruption History
One disruption event: the 27 October 2026 FBI seizure of virtualine.net (Operation Omegaline), preceded by the February 2026 loss of the Railnet backbone and the October 2026 collapse of OMEGATECH routing. The action was a domain seizure only: no arrests, no charges, no sanctions, no server seizures announced, and the operator retained virtualine.org and its Telegram channel. Earlier friction points were blocklisting (Spamhaus/abuse.ch), absorbed via churn, and metaspinner's public disavowal of AS209800. The German upstream aurologic has not de-peered any Virtualine-linked network and was not named in the seizure announcement. [3][4][14][15]
Virtualine is assessed as disrupted but not dismantled. A domain seizure with no arrests, no named operator and no sanctions leaves the operator, the customer base, the payment addresses and one routed ASN (AS209800) intact, and the operator has publicly said it will rebrand. The most likely near-term trajectory is a successor brand within weeks, consistent with the joint November 2025 advisory's finding that a BPH can obtain a new ASN in two to five business days. The structural leverage points are unchanged and now more actionable: (1) the Kentucky/Israel corporate front (Railnet LLC / White Label Networks LLC), which a US criminal case can reach with process; (2) the German upstream aurologic GmbH, still un-actioned and still carrying AS209800; (3) the fraudulent metaspinner registration, with a cooperative victim company on record; and (4) the newly labeled bitcoin addresses (TRM, Chainalysis), which give exchanges a basis to freeze and give investigators a path to the operator through cash-out. Sanctions designation remains the obvious next step and has not happened.
Mandatory Intelligence Gaps
No individual operator, administrator, or handle has been attributed to Virtualine/Railnet. The controlling operator behind the Railnet LLC / White Label Networks LLC chain is unnamed in open source. Highest-priority gap.
TRM Labs and Chainalysis labeled Virtualine's bitcoin addresses in October 2026 and published counterparty shares, but no dollar totals, no cash-out exchanges and no laundering model are public. Monero-side flows remain untraceable.
The DOJ announcement covers one domain. Whether servers, additional domains or wallets were seized is not stated; whether the "protection plan" shell companies and AS209800 are absorbing displaced customers is unmeasured as of 29 October 2026.
Kentucky SoS organizer/officer detail behind Railnet LLC and the specifics of the White Label Networks LLC agency relationship are not captured in open reporting (public-record pull recommended).
Beyond DripHosting and RetryHost, the full set of brands routed through the Railnet backbone and their ownership relationship to Virtualine are unresolved.
Firehol Level 1/2 and abuse.ch Feodo standing for the Virtualine ASNs were not located this pass; direct dataset queries needed.
Several IP-level IOCs carried from the primary research (e.g., 195.211.190[.]189 for Lynx; 91.92.240[.]117 DCRat C2) were not independently re-verified in this pass and are labeled Credible pending direct tracker confirmation.
Whether Virtualine controls any physical hosting (versus reselling broker-sourced IP over German upstreams) is undocumented.
Recent Reporting
Update Pass (29 October 2026)
Status moved from Active to Disrupted. The FBI Washington Field Office and the US Attorney for the Eastern District of Virginia seized the primary storefront domain under Operation Omegaline with German, Dutch and UK partners. The announcement alleges a "BTC [NO-AML]" payment channel to unhosted bitcoin addresses, laundering of proceeds, and knowing retention of a CSAM forum after January 2026 warnings. No operator was named, no charges or sanctions announced. TRM Labs and Chainalysis published address labeling on 28 October; Silent Push published its Operation Omegaline analysis on 27 October. RIPE and RIPEstat queries run for this pass on 29 October 2026 confirm Railnet (AS214943) unrouted since 12 February 2026 with its RIPE object deleted, OMEGATECH (AS202412) visible to a single peer, and AS209800 still routed. The "un-actioned node" finding that defined the July 2026 profile no longer holds; the "no named operator" finding does. [14][15][16][17][18][19]
Follow-On Verification (July 2026)
This profile was built from a primary research document plus a July 2026 follow-on pass. Verified against primary sources: the Virtualine-Railnet-OMEGATECH linkage (Intrinsec May 2026; Spamhaus; Recorded Future Nov 2025); Railnet's ~19 prefixes and ~95% aurologic dependency (Recorded Future BGP data, Aug 28, 2025); the Virtualine Technologies sub-allocation routed through Railnet and the DripHosting/RetryHost downstream brands (RIPE via Recorded Future); the "Railnet LLC operates under Virtualine Technologies, a Russia-based bulletproof hosting provider" characterization (GBHackers, Mar 2025); and the unsanctioned status (no OFAC/EU/UK/AU designation located).
A significant development after the primary research cutoff: Spamhaus (Sept 2025) and Recorded Future (Nov 2025) documented Virtualine Technologies expanding to AS209800 by fraudulently impersonating a legitimate German company, metaspinner net GmbH. metaspinner provided evidence on November 10, 2025 confirming its identity was unlawfully used; the prefixes were later re-described as "LANEDONET." This adds a fraud-based enforcement angle and confirms continued, active expansion.
No arrest, indictment, seizure, or sanctions designation specific to Virtualine, Railnet LLC, White Label Networks LLC, OMEGATECH, or aurologic GmbH was identified in open sources through July 2026. The July 13, 2026 OFAC action (FirstVPN/1VPNS) targeted a different enabler and did not name Virtualine. The un-actioned status is the single most notable standing anomaly.
The DripHosting/RetryHost downstream-brand relationship rests on a single vendor's RIPE reading (Recorded Future). Several IP-level IOCs carried from the primary research were not re-verified this pass and are labeled Credible. No named-operator attribution exists from any source; the operator hero module is intentionally omitted for that reason.
Sources
Citations renumbered for this profile from verified follow-on research. The primary research document (Perplexity Deep Research, BPH_Research_Template_v2) supplied the initial structure and several IOCs; where a claim rests only on that document and was not independently re-verified, it is marked in-line rather than given a numbered web source.