Executive Summary and Provider Overview
Quick-Reference Attributes
| Common Names | Aeza; Aeza Group; AezaNet; aeza.net / aeza.ru; ООО АЕЗА ГРУПП |
|---|---|
| Node Type | Bulletproof Hosting Provider |
| Status | Active - reassessed from Degraded on 29 October 2026. RIPEstat shows AS210644 announcing 316 IPv4 prefixes (94,464 addresses) and AS216246 58 prefixes (14,848 addresses); Qurium counts 536 /24 networks and about 137,000 addresses across Aeza and NetCrafters in September 2026, against roughly 6,400 at end-2022. The Hypercore successor (AS211522) is dissolved and unrouted; the footprint moved back onto the two original ASNs plus NetCrafters OÜ. Aeza registered 57 new IPv4 blocks between July 2025 and October 2026, the latest on 13 October 2026. Three founders remain in Russian detention. [1][2][25][27] |
| Entity Registration Jurisdiction | Russia (RU) - Aeza Group LLC, TIN 7813654490, St. Petersburg (parent). United Kingdom (UK) - Aeza International Ltd (Co. 15109642) and Hypercore Ltd (Co. 16558658). Also Serbia (Smart Digital Ideas DOO) and Uzbekistan (Datavice MCHJ) as successor shells. Hypercore Ltd recorded as dissolved at Companies House on 23 December 2025 (single source). RIPE: AEZA GROUP LLC holds a RIPE NCC LIR organisation record (ORG-AGL50-RIPE, org-type LIR, Zolnaya Street 15, St. Petersburg) created 29 December 2025 and maintained by RIPE NCC's hostmaster maintainer; AS210644 was re-pointed from the UK front to this Russian LIR record on 6 March 2026. Estonia (EE): NetCrafters OÜ (AS203273) receives former Hypercore address space from 6 February 2026 (Qurium). [1][2][3][25][26][27] |
| Infrastructure Hosting Jurisdiction | Primary European footprint in Sweden, Netherlands, and Germany (aurologic GmbH data center, Langen; Hetzner resale); directly controlled nodes in Moscow and St. Petersburg, Russia. [10][11][14][15] |
| Assessed Operator Location | Russia - all six designated operators are Russian nationals; three are in Moscow pre-trial detention, three at large in Russia. [1][2][3] |
| Active Period | Aeza Group LLC incorporated 17 Jun 2021 (marketed launch 26 Dec 2021); predecessor MskHost ~2019 to Sep 2021. [15] |
| Primary ASNs | AS210644 (AEZA-AS, now registered to AEZA GROUP LLC RU in RIPE; 316 prefixes, Oct 2026); AS216246 (RU-AEZA-AS, Aeza Group LLC; 58 prefixes); AS203273 (NetCrafters OÜ, Estonia; 171 prefixes; Aeza-associated migration network per Qurium, CREDIBLE); AS211522 (Hypercore Ltd, former successor; unrouted since 7 February 2026, RIPE object deleted). [10][16][25][27] |
| Upstream Transit | AS30823 aurologic GmbH (Germany, still the dominant upstream of AS210644 and AS203273 in October 2026); AS31500 GlobalNet (RU); AS6939 Hurricane Electric; AS28917 Fiord Networks (LT, Frankfurt, about 212 Aeza prefixes seen September 2026); AS47122 and AS57304 (RU, upstreams of AS216246); AS24940 Hetzner (server resale); AS8218 Zayo. [11][14][25][27] |
| Abuse Contact | abuse@aeza.net / abuse@aeza.ru (RIPE role AR79375-RIPE); NOC noc@aeza.ru, +7 800 200 6013, +7 965 013 5518 (RIPE org and role NT5020-RIPE, created 29 December 2025); support via @aezasupport_bot (Telegram). [16][27] |
| Sanctions | SANCTIONED OFAC SDN (1 Jul 2025 and 19 Nov 2025); UK FCDO/OFSI (19 Sep 2025 and 19 Nov 2025); Australia DFAT (19 Nov 2025). EU: no designation as of 29 October 2026. [1][2][5][14][25] |
| Blocklist Standing | Spamhaus ASN-DROP: AS210644 LISTED ("under control of cyber-criminals"); 3,000+ ThreatFox IOCs on AS210644 over 12 months. [16][23] |
| Designated Crypto | TU4tDFRvcKhAZ1jdihojmBWZqvJhQCnJ4F (TRON), OFAC-designated 1 Jul 2025; $350k+ received; Garantex pathway. [3][7][8] |
| State Nexus Tier | Probable Cooperation (Tier 3 of 4) - assessed; based on confirmed bulletproof hosting for the Social Design Agency (SDA) / Doppelgänger and ~4 years of non-enforcement in Russia. [5][12][13] |
Overall Assessment
Aeza Group is a St. Petersburg-based bulletproof hosting (BPH) provider that presented publicly as a low-cost, high-performance VPS/VDS and dedicated-server business while functioning as core infrastructure for ransomware, infostealer, darknet-market, and Russian state-aligned disinformation operations. OFAC, which designated the group on 1 July 2025, described Aeza as a BPH service that "allows cybercriminals to avoid law enforcement while renting IP addresses, servers and domains" and specifically named the Meduza and Lumma infostealer operators, BianLian ransomware, RedLine infostealer panels, and the BlackSprut darknet drug marketplace as hosted activity. [1]
The provider is the assessed successor to MskHost, a predecessor BPH brand founded circa 2019 by Yurii Bozoyan and taken offline by hacktivists in September 2021. Aeza Group LLC was incorporated in June 2021 with Bozoyan, Arsenii Penzev, and Igor Knyazev each holding 33%. Its business model deliberately routed criminal clients through a downstream reseller chain (LetHost, ZeroHost, and others), which advertised the "bulletproof" property to end users while Aeza maintained plausible deniability at the core ASN level. [1][14][15]
Aeza was assessed as Degraded in the July 2026 profile; as of October 2026 it is assessed Active and larger than before sanctions (see the paragraph that follows). Russian authorities arrested Penzev, Bozoyan, and Gast in February/April 2025 (charged with narcotics and organized-crime offenses tied to BlackSprut, not cybercrime), and OFAC/UK/Australia sanctions followed. Within nineteen days of the July 2025 OFAC action, Silent Push detected roughly 2,100 IP addresses migrating from AS210644 to the newly registered AS211522 (Hypercore Ltd), and the November 2025 tri-lateral action designated Hypercore plus Serbian and Uzbek successor shells and two additional operators (Makarov, Zakirov). The European Union imposed no sanctions, and Recorded Future described Aeza as "one of the most significant sources of malicious infrastructure" as recently as November 2025. The single largest structural leverage point remains the group's dependency on German upstream aurologic GmbH for its European footprint. [2][10][11][14]
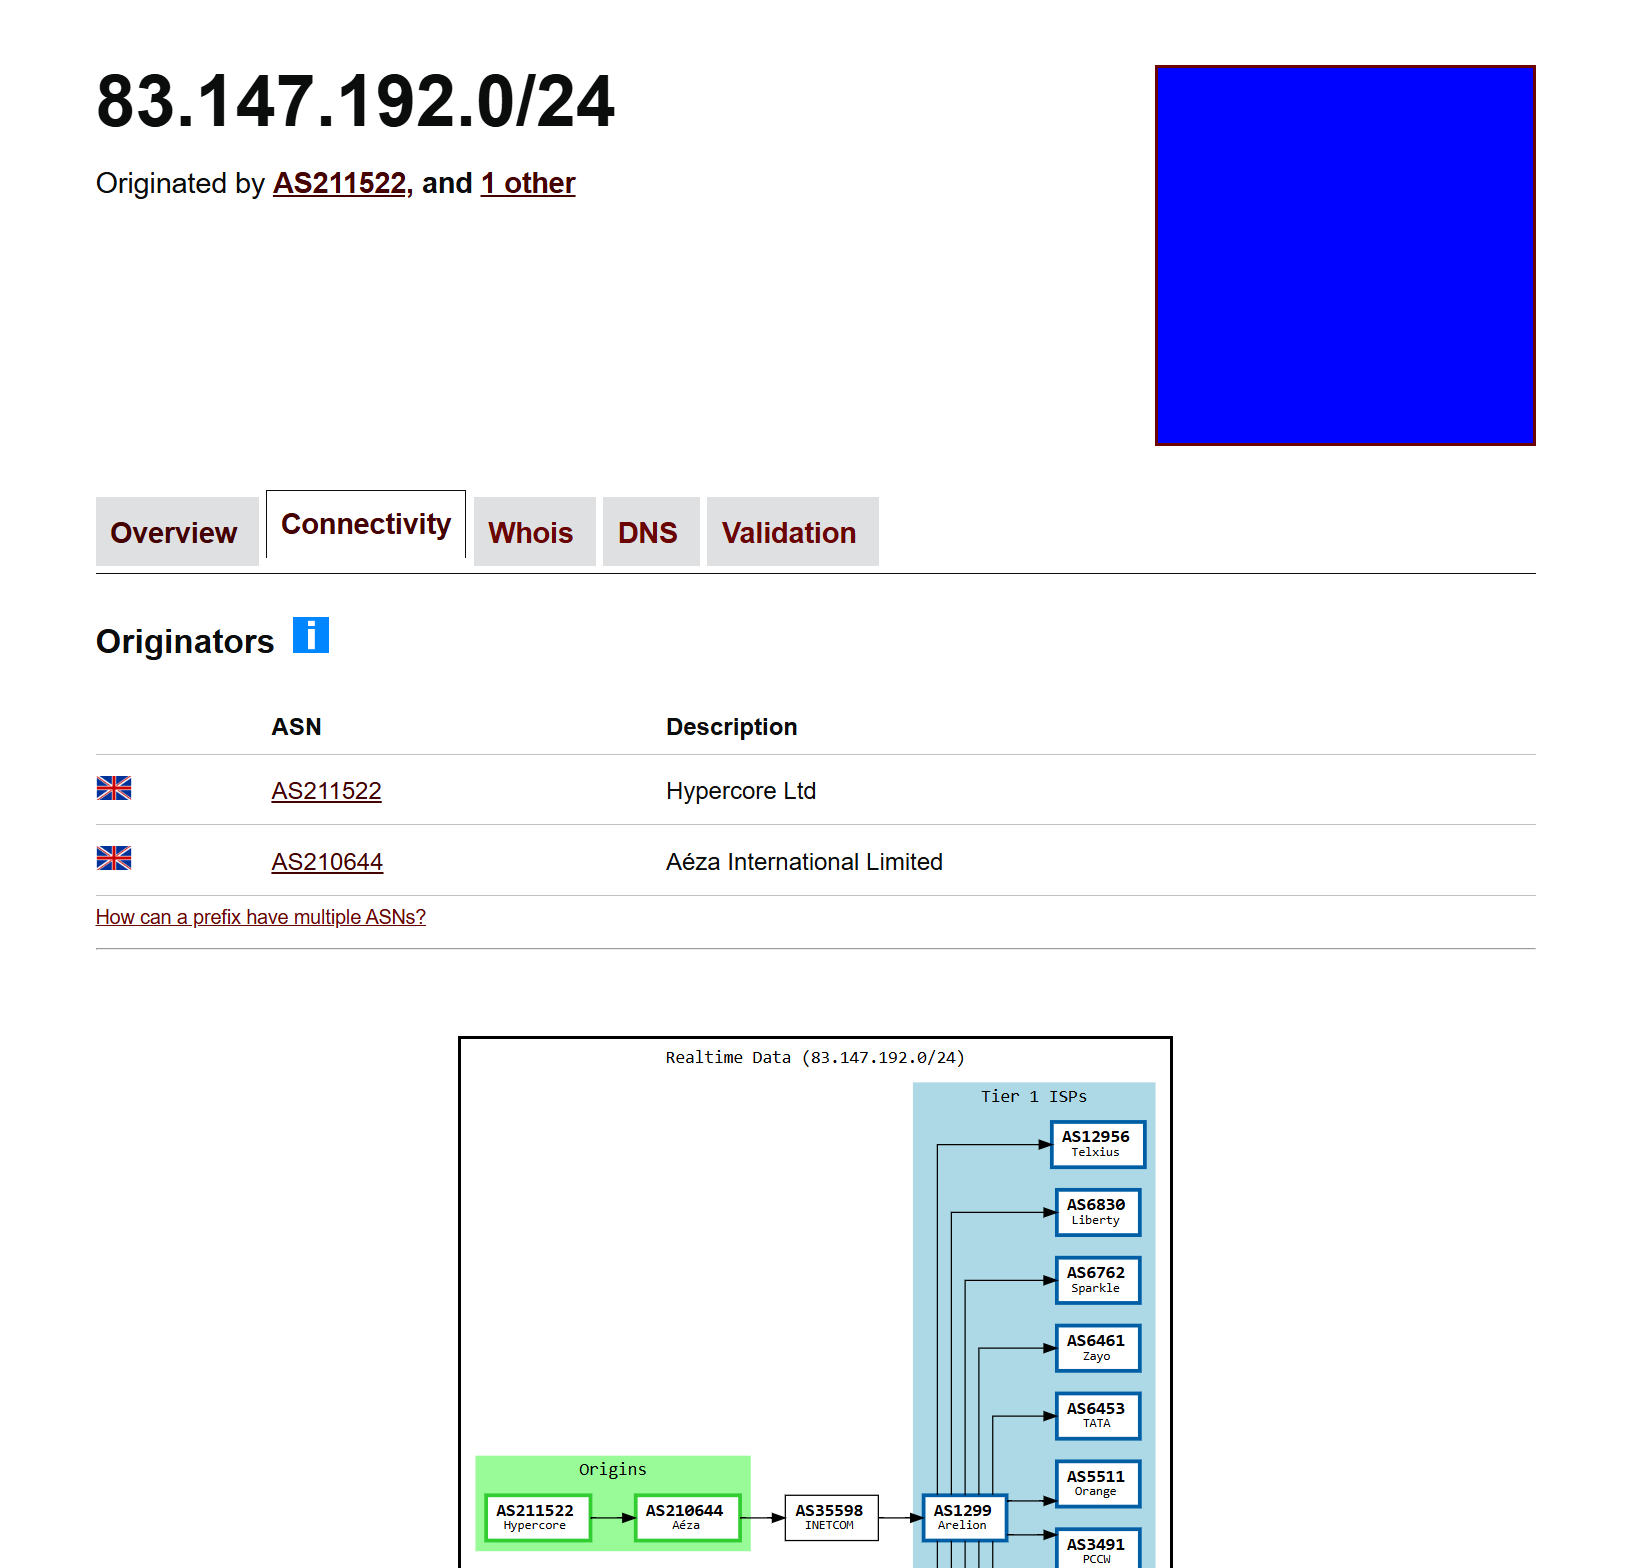
Confirmed October 2026 reassessment. The Hypercore route proved temporary: Hypercore Ltd was recorded as dissolved on 23 December 2025, AS211522 stopped announcing on 7 February 2026 and its RIPE registration has since been deleted. The address space did not disappear. From 6 February 2026 former Hypercore prefixes (for example 83.147.192.0/24) appear under NetCrafters OÜ (AS203273, Estonia), and the two original Aeza ASNs grew: on 29 October 2026 AS210644 announces 316 IPv4 prefixes and AS216246 58, together about 109,000 addresses, with NetCrafters adding 171 prefixes. Qurium's September 2026 count is 536 /24 networks and about 137,000 addresses, roughly twenty times the end-2022 baseline. In the RIPE database the maintainer lir-ru-aezagroup-1-MNT now controls 245 objects, 57 of them IPv4 blocks registered after the 1 July 2025 OFAC action, the latest on 13 October 2026, and AEZA GROUP LLC itself holds a RIPE NCC LIR organisation record created 29 December 2025. aurologic remains the dominant upstream. Two rounds of US, UK and Australian sanctions have therefore not reduced Aeza's ability to obtain or route IP space; what they changed is the corporate wrapper. [25][26][27]
Lineage and Organizational Heritage
Predecessor and Sibling Analysis
Aeza is assessed as the direct successor to MskHost (MSK.host), a bulletproof and abuse-tolerant hosting provider founded circa 2019 by Yurii Bozoyan and known for launching DDoS attacks against competing hosts. MskHost was taken offline by hacktivists "who had enough" in September 2021, per researcher compilation at aeza-gang.com and corroborating forum records. The same operator pool, principally Bozoyan and Penzev, incorporated Aeza Group LLC on 17 June 2021 and marketed a public launch date of 26 December 2021. [15]
Confirmed Four independent evidentiary pillars support this lineage: (1) Infrastructure continuity - shared server hardware patterns (Threadripper 3990X, later i9-14900K) appearing at MskHost-linked LetHost; (2) Personnel continuity - Bozoyan confirmed as founder of both, Penzev present at Aeza founding; (3) Forum corroboration - multiple LowEndTalk / searchengines.guru participants stated "mskhost стал aeza" (MskHost became Aeza), and one user told Aeza directly in 2024 "I lost a lot of money because of your past project MskHost"; (4) Client migration - MskHost clients migrated to Aeza. [15][18][19]
Brand, Entity, and Sibling Structure
| Entity / Brand | Jurisdiction / Identifier | Role | Active Window | Confidence |
|---|---|---|---|---|
| MskHost (MSK.host) | Russia | Predecessor BPH brand; owner Bozoyan | ~2019 to Sep 12, 2021 | Confirmed |
| Aeza Group LLC (ООО АЕЗА ГРУПП) | Russia; TIN 7813654490; AS216246 | Russian parent entity | Jun 17, 2021 to present | Confirmed |
| Aeza International Ltd | UK; Co. 15109642; AS210644 | UK front; leases IP to cybercriminals per OFAC | Sep 1, 2023 to present | Confirmed |
| Aeza Logistic LLC | Russia; TIN 7810965578 | 100%-owned subsidiary | Sep 27, 2024 to present | Confirmed |
| Cloud Solutions LLC (Облачные Решения) | Samara, Russia; TIN 6312219617 | 100%-owned subsidiary | Jul 23, 2024 to present | Confirmed |
| Hypercore Ltd | UK; Co. 16558658; AS211522 | Post-sanctions successor infrastructure vehicle | Jul 2025 to present (designated Nov 19, 2025) | Confirmed |
| Smart Digital Ideas DOO | Belgrade, Serbia; TIN 113294246 | Successor shell | 2025 (designated Nov 19, 2025) | Confirmed |
| Datavice MCHJ | Tashkent, Uzbekistan; TIN 312252645 | Successor shell | Jul 2025 (designated Nov 19, 2025) | Confirmed |
| Shelter LLC | Russia; TIN 5049025855; AS211409 | Ecosystem-linked; hosted Lumma/Meduza/Mystic C2 | Researcher-identified | Credible |
| TNSecurity Ltd | UK; Co. 15103352 | Reseller/distributor; "prefix swapping with AEZA"; owner Anastasija Berezina (Latvia) | Researcher-identified | Credible |
| Liber Systems | UK; Co. 11405895 | Managed 2nd-level domains for Doppelgänger network | Researcher-identified | Credible |
| LetHost / ZeroHost | Russia | Downstream resellers on Aeza hardware; advertised "bulletproof" | ~2022 to 2024 | Credible |
Additional UK entities identified by researchers as part of the network include AEZA GROUP LIMITED (Co. 15065828), AEZATRADE LIMITED (Co. 15172068), and QWINS LTD (Co. 16072422). Researcher-identified sibling ASNs include AS210352 (Partner LLC), AS211409 (Shelter LLC), AS209224 (CYBERHUB-AS), and AS216319 (CHROMIS IT LTD). [15]
Operator Profiles
Six individuals have been sanctioned across the July and November 2025 actions; three were arrested by Russian law enforcement in early 2025. All are Russian nationals. The escalated operator module appears above the fold in Section 01. Detailed profiles follow.
2.1 Yurii Meruzhanovich Bozoyan
| Handles / Aliases | "Yuri Bozoyan"; general director; no confirmed public pseudonym |
|---|---|
| DOB / Nationality | 30 January 1992; Russian |
| Current Location | Pre-trial detention, Moscow (since April 2025) |
| Role | General Director; 33% owner; founder of predecessor MskHost (~2019) |
| Legal Status | Arrested April 2025; charged under RF Articles 210 (organized criminal group) and 228.1 (drug trafficking); faces up to 20 years |
| Sanctions | OFAC SDN 1 Jul 2025 (Tax ID 780538991581); UK 19 Sep 2025. OFAC basis: "helped manage the finances of Aeza Group and was similarly arrested for his involvement in Blacksprut." |
| Notes | Befriended Penzev 2018-2019 when the then-16-year-old Penzev proposed renting servers; invested 400,000 rubles as founding partner. Court published photos of Bozoyan in a detention cell. |
2.2 Arsenii Aleksandrovich Penzev
| Handles / Aliases | "Arseny Penzev"; email aezagroup@gmail.com; domain aezadns.com |
|---|---|
| DOB / Nationality | 27 October 2002; Russian (age 21 at arrest) |
| Current Location | Pre-trial detention, Moscow (since April 2025) |
| Address | Leninskiy str. 64, 1, A, 766, St. Petersburg 198335, Russia |
| Role | CEO; 33% owner |
| Legal Status | Arrested April 2025; charged under RF Articles 210 and 228.1 |
| Sanctions | OFAC SDN 1 Jul 2025 (Tax ID 780721423242); UK 19 Sep 2025. OFAC basis: "has been involved in multiple bulletproof hosting and illicit drug marketplace businesses"; arrested for placement of BlackSprut onto Aeza infrastructure. |
| Notes | Youngest operator; publicly represented Aeza as legitimate and apolitical in the mid-2024 VSquare interview and claimed the group responded to all complaints. |
2.3 Vladimir Vyacheslavovich Gast
| Handles / Aliases | None confirmed (myrotvorets.center profile exists) |
|---|---|
| DOB / Nationality | 6 May 1999; Russian |
| Current Location | Detained (arrested April 2025) |
| Role | Technical Director; manages internal network; DDoS/botnet lead |
| Legal Status | Arrested April 2025; charged |
| Sanctions | OFAC SDN 1 Jul 2025 (Tax ID 860243420832); UK 19 Sep 2025. OFAC basis: "manages Aeza Group's internal network and oversaw the technical details of placing Blacksprut on Aeza Group infrastructure." |
| Notes | Described by researchers as "the key link" in Aeza DDoS operations; "together with Penzev … created and use botnets." DDoS attacks attributed to Aeza reportedly continued after his arrest, indicating other accomplices remain active. |
2.4 Igor Anatolyevich Knyazev
| Handles / Aliases | None confirmed |
|---|---|
| DOB / Nationality | 26 July 1986; Russian |
| Current Location | At large (Russia) |
| Role | 33% owner; acting director during absence of Bozoyan and Penzev |
| Legal Status | Not criminally charged in Russian proceedings (per available information); OFAC-designated |
| Sanctions | OFAC SDN 1 Jul 2025 (Tax ID 780532513677); UK 19 Sep 2025. OFAC basis: "is managing the company during the absence of Penzev and Bozoyan." |
| Notes | Held operational control during the critical post-arrest period before the July 2025 sanctions. |
2.5 Maksim Vladimirovich Makarov
| Handles / Aliases | None confirmed |
|---|---|
| DOB / Nationality | 23 March 1989; Russian |
| Current Location | At large (Russia) |
| Role | New Director of Aeza (installed after original leadership arrested) |
| Sanctions | OFAC SDN 19 Nov 2025 (Tax ID 244309586068; Passport 772555187); UK 19 Nov 2025. OFAC basis: "new director of Aeza" who "made key decisions regarding Aeza Group's attempt to evade sanctions." |
2.6 Ilya Vladislavovich Zakirov
| Handles / Aliases | None confirmed |
|---|---|
| DOB / Nationality | 20 November 1999; Russian |
| Current Location | At large (Russia) |
| Role | Associate; established successor companies and payment channels |
| Sanctions | OFAC SDN 19 Nov 2025 (Tax ID 165504427793). OFAC basis: "helped establish new companies and payment methods to obfuscate Aeza's continuing activity." |
Non-Designated Front Persons
Marat Timurov (Uralsk, M. Ihsanov str. 45, Kazakhstan) is identified by researchers as the nominal front person for Aeza International Ltd (UK Co. 15109642); not OFAC-designated as of the record date. Separately, open reporting attributes the registration of Hypercore Ltd to a "Patryk Drozda" two days after the July 2025 sanctions. [SINGLE SOURCE] This registrant name should be treated as CREDIBLE pending Companies House corroboration; it does not appear in the OFAC designation text. [15]
Disputed Assessments
Penzev publicly disputed the Doppelgänger and state-nexus allegations (see Section 03 verbatim copy), and Aeza's official agent characterized reseller connections (LetHost/ZeroHost) as mere IP-transit relationships terminated after complaints. These claims are contradicted by (a) OFAC's finding that Bozoyan and Penzev "began to provide Blacksprut with services in 2023," and (b) forum evidence of identical server hardware appearing simultaneously at Aeza and the resellers. The name "Yuri" vs. "Yurii" for Bozoyan varies between OFAC (Yurii) and secondary reporting; treated as the same individual. [1][14][15]
Operational and Business Model
Service Model
Aeza publicly marketed itself as a high-performance, affordable VPS/VDS and dedicated-server provider for legitimate customers, developers, and VPN users. Advertised products included KVM VPS on AMD Ryzen 9 7950X3D/9950X with NVMe storage from roughly €4.94/month, dedicated Threadripper and i9-class servers from about €200/month, anti-DDoS on all plans, and locations spanning Moscow, St. Petersburg, Stockholm, Helsinki, Amsterdam, Vienna, Paris, Frankfurt/Falkenstein, London, Hong Kong, and Los Angeles. Behind this commercial face, OFAC assessed Aeza as a de facto BPH provider that "allows cybercriminals to avoid law enforcement while renting IP addresses, servers and domains used for disseminating malware, supporting darknet markets and carrying out other tasks related to fraud and cyberattacks." [1]
Plausible deniability was maintained by routing malicious clients through a downstream reseller chain rather than direct onboarding (see reseller chain below). This architecture is the primary mechanism by which Aeza insulated its core ASNs from direct attribution. [1][14]
Verbatim Advertising Copy
"Our advantages: Activation within 60 seconds of payment; 24/7/365 chat support; AntiDDoS protection on all servers; Hourly rate option from 0.02€/hour."
"Available payment methods: Bank cards of any country (Visa/Mastercard/World and others); Cryptocurrency (Bitcoin, Litecoin, Dogecoin, BTC Cash, USDT and others); E-wallets (YouMoney, PerfectMoney and others)."
"More than 80% of our clients use the servers for VPN, to bypass blocking and get access to independent information."
"We have not received any complaints about 'twin sites'. And those AS that were served through us we have switched off, but even during their work we received almost no complaints."
"We have nothing illegal located on our site, and we always respond to all complaints."
Aeza did not openly market itself as "bulletproof" in its own storefronts. Its resellers (LetHost, ZeroHost, and others on Aeza infrastructure) advertised "bulletproof" services to end criminal customers. The VSquare investigation confirmed: "Aéza's resellers advertised its services as 'bulletproof.'" [14]
Pricing (Documented Examples)
| Tier | Config | Price |
|---|---|---|
| Standard VPS (shared, Ryzen 9 9950X) | 2 GB / 1 core / 30 GB NVMe | €4.94/mo |
| Standard VPS | 8 GB / 4 cores / 120 GB | €19.77/mo |
| Standard VPS | 32 GB / 16 cores / 480 GB | €79.09/mo |
| Dedicated VDS (dedicated CPU) | 2 GB / 1 core / 30 GB | €7.07/mo |
| Dedicated servers | Threadripper / i9-class | from ~€200/mo |
| Entry hourly rate | advertised on LowEndTalk | €0.02/hr |
| Historical promo (Aug 2022) | 1 core / 8 GB / 20 GB / 100 Mbps | 99 RUB/mo (~€1.60) |
Onboarding
Aeza operated an open-signup model with no identity verification. A third-party review site documented that "the service supports anonymous registration, no real-name verification, and accepts cryptocurrency payments." Penzev framed equal treatment of all clients (including censorship-evading and opposition-linked projects) as a neutral, apolitical posture; no vetting of client intent was performed. [14]
Downstream Reseller Chain
- LetHost / ZeroHost ran "on your hardware" per direct LowEndTalk accusations. A forum participant reported contacting St. Petersburg law enforcement about the Aeza connection in 2022 and being told "in Russia it is not forbidden to keep such hosting." The FBI reportedly later shut down LetHost. Aeza's agent claimed these were merely IP-transit clients cut off after complaints, disputed by evidence of identical hardware at both operations. [14][19]
- TNSecurity Ltd (UK): researcher-identified downstream distributor running "prefix swapping with AEZA."
- Shelter LLC (AS211409): hosted C2 for Lumma, Meduza, and Mystic stealers.
- Doppelgänger's European infrastructure was accessed through this chain, with Aeza upstream while UK shells (TNSecurity, Liber Systems) appeared as direct operators. [12][13]
Russian IT-law specialists consulted by investigace.cz noted that "legal liability may extend to the original hosting providers, not just the resellers." [14]
Abuse Handling and LE Posture
Stated posture: "We always respond to all complaints" (Aeza agent, July 2024); Penzev: "If we receive a complaint from Roskomnadzor, we forward it to the client." Documented behavior contradicts this: Aeza hosted BlackSprut for roughly two years before Russian action; Spamhaus flagged LetHost/ZeroHost-linked subnets; and OFAC found Bozoyan and Penzev "began to provide Blacksprut with services in 2023." Penzev's claim that Aeza terminated the BlackSprut reseller "because of the large number of reports we received from Spamhaus" is directly contradicted by the OFAC finding. Support ran via a 24/7 Telegram bot (@aezasupport_bot), a ticket panel, and RIPE abuse contacts abuse@aeza.net / abuse@aeza.ru. [1][14]
OPSEC
Multi-jurisdiction incorporation (RU LLC, UK Ltd, plus post-sanctions Serbia and Uzbekistan shells), reseller abstraction, anonymous crypto/e-wallet payments, and separation between Russian-controlled hardware and European delivery infrastructure. The principal OPSEC failure was operator concentration in Russia: all six designated operators are Russian nationals, and three founders were arrested domestically. [1][2][14]
Technical Capabilities and Infrastructure Footprint
Autonomous Systems
| ASN | Registered Name | Reg. Country | Active Window | Notes |
|---|---|---|---|---|
AS216246 | Aeza Group LLC (RU-AEZA-AS) | Russia (RIPE) | Sep 27, 2023 - active | 58 IPv4 prefixes, 14,848 addresses announced 29 Oct 2026 (RIPEstat); org ORG-AGL40-RIPE, Moskovsky prospect 97A, St. Petersburg; upstreams AS57304, AS47122 CYBERFIRST, AS31500 GlobalNet; also provides transit to AS210644 and AS203273; RIPE object modified 28 Sep 2026 [27] |
AS210644 | AEZA GROUP LLC (AEZA-AS); formerly Aeza International Ltd | Russia (RIPE) | 2021 - active | 316 IPv4 prefixes, 94,464 addresses announced 29 Oct 2026 (RIPEstat); Spamhaus ASN-DROP listed. RIPE org re-pointed on 6 Mar 2026 from the UK front (Aeza International LTD, 311 Shoreham Street, Sheffield) to ORG-AGL50-RIPE, AEZA GROUP LLC, St. Petersburg, a RIPE NCC LIR record created 29 Dec 2025. Dominant upstream aurologic AS30823 (RIPEstat neighbour power 630), then GlobalNet AS31500 and Hurricane Electric AS6939 [27] |
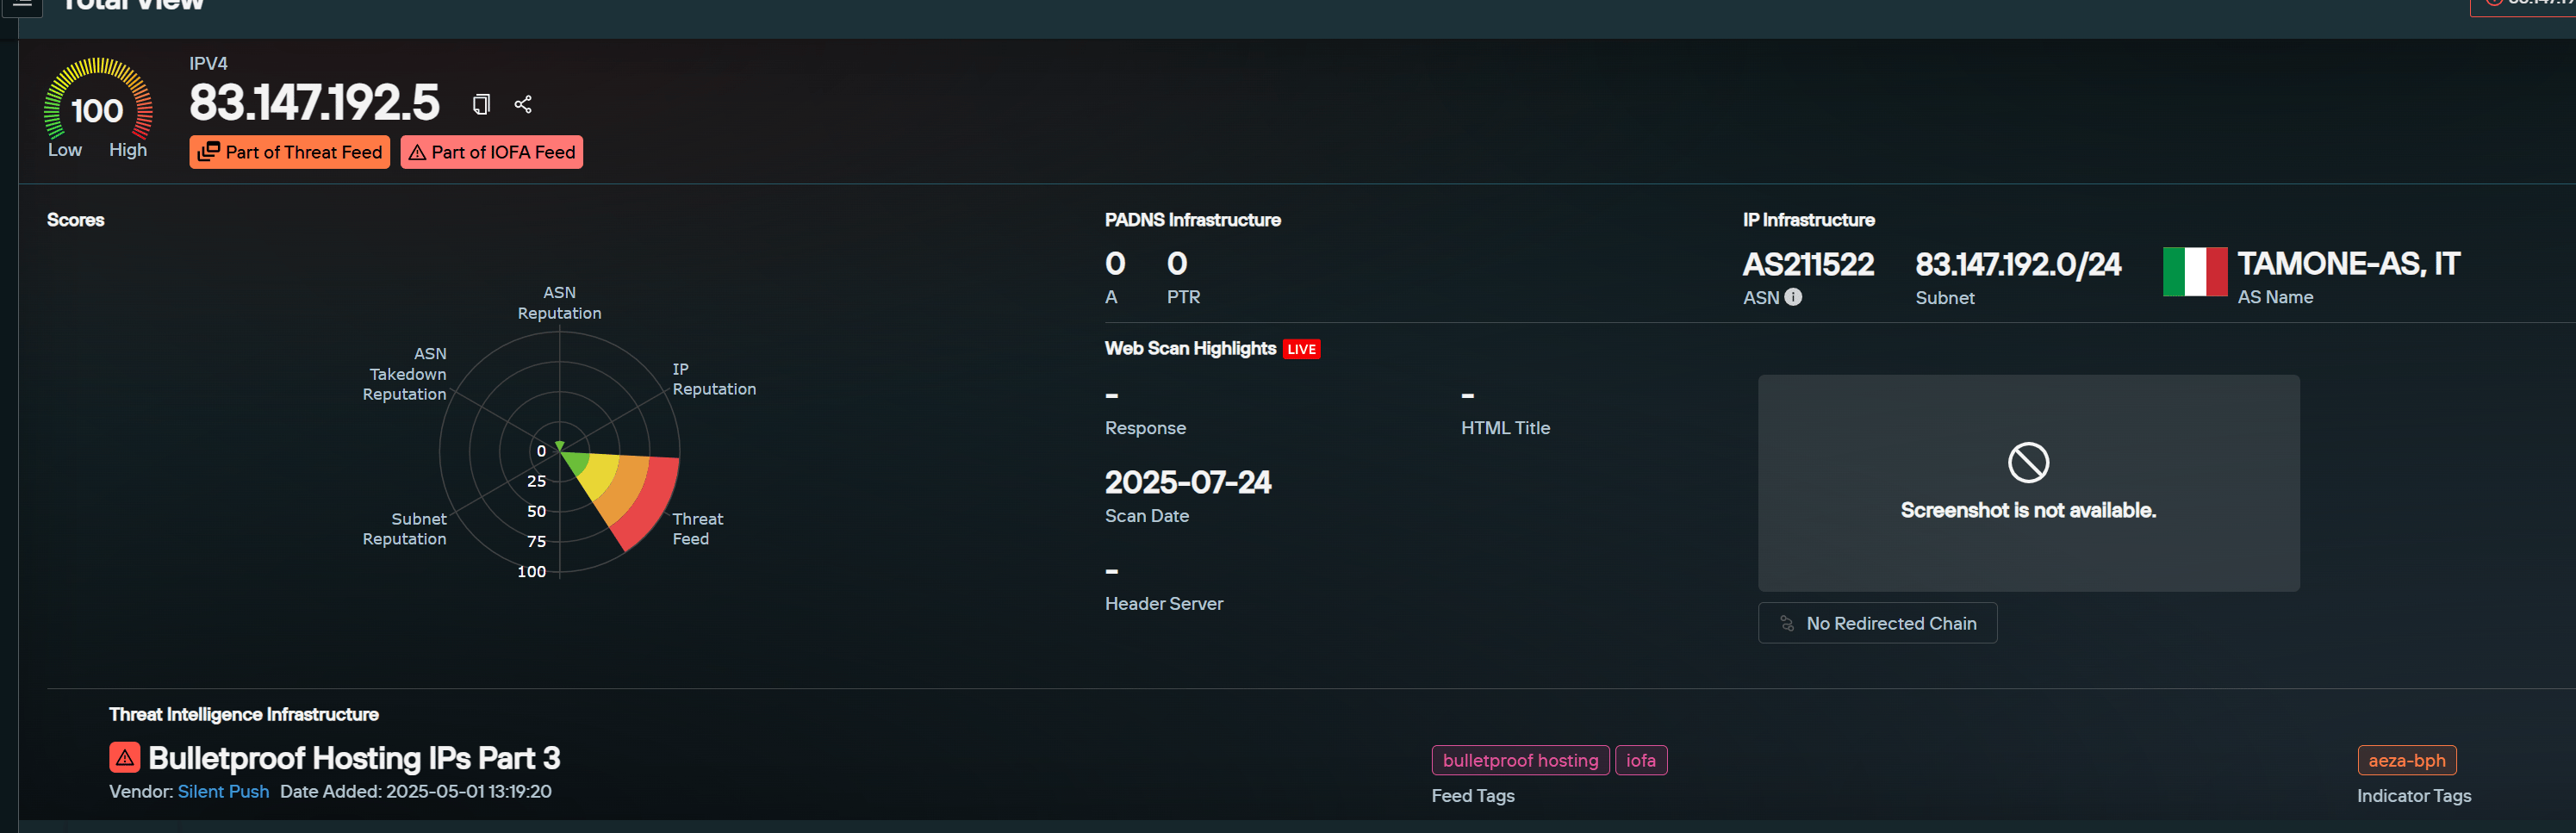
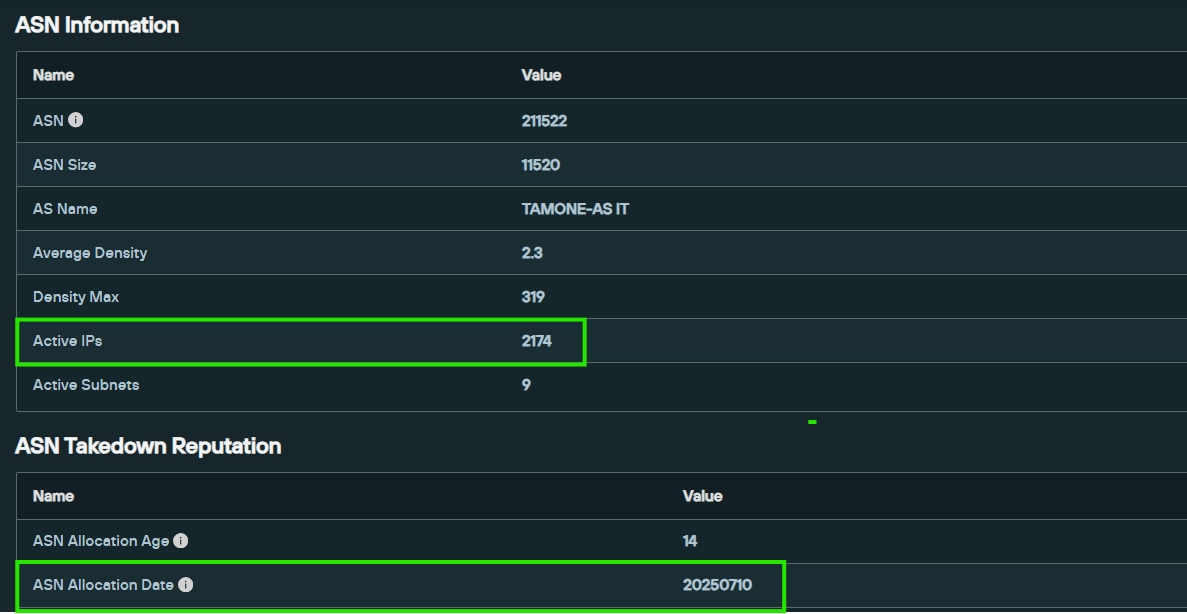
AS211522 | Hypercore Ltd | UK | Jul 10, 2025 - Feb 7, 2026 | Post-sanctions successor; 2,100+ IPs migrated from AS210644 starting Jul 20, 2025. OFAC-designated 19 Nov 2025; Companies House dissolution recorded 23 Dec 2025 (single source); last prefix announcement 7 Feb 2026; no aut-num object in RIPE as of 29 Oct 2026. 83.147.192.0/24 is now announced by AS203273 [2][26][27] |
AS203273 | NetCrafters OÜ | Estonia | ASN first seen 2016; Aeza-associated from Feb 6, 2026 | Credible Qurium (Oct 2026) identifies NetCrafters as the latest migration network for Aeza address space, 118 prefixes and 30,208 addresses in Sep 2026; RIPEstat 29 Oct 2026: 171 IPv4 prefixes, 44,288 addresses; upstreams aurologic AS30823, Hurricane Electric AS6939, AS207208, AS57304, and transit from Aeza's own AS216246. Whether NetCrafters is Aeza-controlled or an independent lessee is not resolved [25][27] |
RIPE abuse contact (AS210644): abuse@aeza.net. Registration verification (29 Oct 2026): AS210644 and AS216246 confirmed live in the RIPE database; AS211522 returns no object. The AS210644 to AS211522 migration of July 2025 is corroborated across Silent Push, bgp.tools, IPinfo, and RIPEstat. The registered organisation for AS210644 is now AEZA GROUP LLC (St. Petersburg), not the Sheffield front. [10][16][24][27]
Full RIPE Footprint (Maintainer Analysis)
Confirmed Inverse lookup on the operator maintainer lir-ru-aezagroup-1-MNT on 29 October 2026 returns 245 objects: 2 ASNs (AS210644, AS216246), 42 legacy ranges, 147 ASSIGNED PA, 29 SUB-ALLOCATED PA, 20 IPv6 assignments, and one IPv6 allocation direct from RIPE NCC (2a01:e5c0::/29, ALLOCATED-BY-RIR to ORG-AGL50-RIPE, object dated 6 March 2026). The maintainer is in RIPE NCC's standard LIR format, which indicates a direct RIPE NCC membership held by AEZA GROUP LLC. 57 IPv4 blocks were created after the 1 July 2025 OFAC designation, in six clusters: [27]
| Created | Blocks | Ranges and netnames | Co-maintainer / lessor signal | Routed by (29 Oct 2026) |
|---|---|---|---|---|
| 14 Jul 2025 | 16 | 213.165.32.0 to 213.165.49.0 (/24s), Aeza-Network, -Stockholm, -Paris (SE, FR) | aeza-mnt | AS210644 |
| 15 to 18 Dec 2025 | 9 | 213.21.229.0 to 213.21.254.0 (/24s), AEZA-SE (SE) | LV-VERNET-HM-MNT (Latvia) | AS210644 |
| 20 May 2026 | 6 | 94.228.162.0 to 94.228.165.0, 94.228.172.0, 178.236.250.0 (/24s), Vienna, London, Moscow | none listed | AS210644 |
| 27 May 2026 | IPv6 | 2a14:a084::/32 AEZA-NETWORK-WARSAW plus 13 /36 assignments (Moscow, SPB) | LocalNCC-mnt | not checked |
| 8 to 10 Jun 2026 | 21 | 45.136.175.0, 45.136.228.0, 45.137.60.0, 45.137.81.0, 45.140.13.0, 45.141.177.0, 45.145.13.0, 45.145.14.0, 45.146.131.0, 45.151.101.0, 45.151.102.0, 45.152.198.0, 45.155.71.0, 94.228.169.0, 94.228.170.0, 178.236.246.0 to 178.236.248.0, 178.236.251.0, 178.236.252.0, 178.236.255.0 (/24s), Helsinki, Stockholm, Moscow, Amsterdam, Vienna | sc-rapidseedbox-1-mnt (RapidSeedbox) on the 45.x blocks | AS210644 (EU), AS216246 (Moscow) |
| 28 Sep to 13 Oct 2026 | 5 | 176.124.223.0/24 Aeza-Network-RU; 94.228.173.0/24, 94.228.175.0/24, 178.236.242.0/24 Moscow; 195.88.92.0/23 RU-AEZAGROUP (ASSIGNED PI, country GB) | Renets-mnt on 176.124.223.0 | AS216246; 195.88.92.0/23 not yet announced (staged capacity) |
Confirmed The LIR organisation record lists 21 referencing maintainers (mnt-ref), including INTERLAN, NETERRA, QWARTA, WEBROCKET, IROST, Renets, LocalNCC, ROSNIIROS and sistemallc: the set of LIRs and brokers entitled to assign space to Aeza. This matches Qurium's finding that eleven LIRs supply about two-thirds of Aeza's addresses (Plant Holding GmbH, Axiom Asia Services, Prostie Reshenia/WebRocket, RapidSeedbox, Technology Enriched Company FZCO, Oner Investments, Andwase Limited, FREEnet, IROST, Digital Network/IPPort, Pronet). Analyst Inference Blocks registered in clusters days apart, with netnames pre-assigned to European cities, indicate planned capacity build-out rather than organic growth; the unannounced 195.88.92.0/23 registered 9 October 2026 is staged capacity. [25][27]
Threat Intelligence Standing of the 57 Post-Sanctions Blocks
Confirmed Checked 29 October 2026 by direct API query of every address in the 57 blocks (14,734 addresses) against ThreatFox and URLhaus, and by AbuseIPDB check-block per /24 (30-day window). 29 of 57 blocks carry at least one post-registration signal; 28 carry none. [28]
| Feed | Result | Detail |
|---|---|---|
| ThreatFox (C2 IOCs) | 11 C2 hosts in 11 blocks | PureRAT (45.141.177.223, three ports, 21 to 22 Oct 2026); Vidar (45.140.13.203, 17 Oct 2026); Mirai (94.228.175.10, 11 Oct 2026, in a block registered 2 Oct 2026); Quasar RAT (45.137.81.207, Sep 2026); Sliver (213.165.37.30, Aug 2026; 213.21.254.240, Jun 2026); BianLian (213.165.40.206, Jun 2026); Cobalt Strike (178.236.252.244 and 45.151.101.97, May to Jun 2026); AsyncRAT (178.236.252.244); AdaptixC2 (45.151.102.251, Jun 2026); one unclassified C2 (213.165.42.57, Jul 2026). The BianLian hit matches a client OFAC named in the July 2025 designation. |
| URLhaus (malware distribution) | 7 hosts in 7 blocks with URLs added after Aeza registered the block | 213.21.252.63 (15 URLs from 22 Dec 2025, four days after registration), 213.21.229.201 (13 URLs from 17 Dec 2025), 178.236.246.159 (14 URLs, Jun 2026), 45.137.81.201 (5 URLs, Jun 2026), 45.152.198.90 (Aug 2026), 213.21.233.188 and 213.21.250.7 (May to Jun 2026). A further 23 hosts in six blocks (94.228.162 to 170.x, 178.236.247.x) carry only 2023 to 2024 entries that predate Aeza's registration and belong to the previous holder; they are excluded. |
| AbuseIPDB (30 days) | 42 of 58 /24s checked: 25 reported addresses, 65 reports; 23 subnets with no reports | Highest confidence 94.228.172.0/24 London (score 57, 12 reports) and 45.141.177.0/24 Stockholm (score 50, the PureRAT host block). 16 subnets, mainly the June 2026 Moscow and Stockholm blocks and all five Sep to Oct 2026 blocks, were not reached before the free tier's daily cap and are pending. |
Analyst Inference Time-to-abuse is short: C2 and malware-distribution entries appear within days of registration (URLhaus four days after the December 2025 AEZA-SE blocks; Mirai nine days after the 2 October 2026 Moscow block). The 28 blocks with no signal include the five newest registrations and the unannounced 195.88.92.0/23, consistent with staged capacity not yet populated. The malware mix (PureRAT, Vidar, Sliver, Cobalt Strike, AsyncRAT, Quasar, AdaptixC2, BianLian, Mirai) is the same C2-and-stealer profile OFAC cited in 2025, now running on address space acquired after the designation. [28]
IP Ranges and Geographic Footprint
- AS210644 (Aeza International): primary footprint in Sweden, with additional presence in the Netherlands and Germany, plus smaller footprints in 10+ countries (Finland, Austria, France, UK). [10][11]
- AS216246 (Aeza Group): Russia-registered; ~26 IPv4 prefixes, ~6,656 addresses (late 2025); 58 prefixes, 14,848 addresses on 29 October 2026. [27]
- Ecosystem total (pre-migration): ~100,000+ IPs; Qurium estimated Doppelgänger-associated infrastructure at 300+ prefixes and 100,000 IPs. [12]
- Ecosystem total (September 2026, Qurium): 536 IPv4 /24 networks, about 137,216 addresses (AS210644 and AS216246: 418 prefixes, 107,008 addresses; NetCrafters AS203273: 118 prefixes, 30,208 addresses), against 25 prefixes and about 6,400 addresses at end-2022. [25]
- Migrated example host:
83.147.192[.]5(subnet 83.147.192.0/24 announced by both AS210644 and AS211522 in July 2025; announced by NetCrafters AS203273 on 29 October 2026). [10][27]
Physical data centers: Europe (primary) - aurologic GmbH facility, Robert-Bosch-Str. 25, 63225 Langen, Germany; Russia - Moscow and St. Petersburg nodes (directly controlled). European servers are primarily sourced through Hetzner resale and aurologic colocation. [11][15]
Upstream Transit Provider Chain
| Upstream | Relationship | De-peering Status |
|---|---|---|
AS30823 aurologic GmbH (Langen, DE) | Primary European upstream + colocation | NOT terminated as of 29 Oct 2026: RIPEstat shows aurologic as the dominant upstream of both AS210644 and NetCrafters AS203273; Qurium (Oct 2026) still lists it as upstream, visible via Equinix Frankfurt and Hetzner Helsinki. Recorded Future noted aurologic "defended" the relationship; Qurium: Aeza "enabled by connectivity suppliers such as Aurologic in Germany continue operating malicious infrastructure" |
AS24940 Hetzner Online GmbH (DE) | Server resale ("All our European VPS are hosted on servers from Hetzner," Aeza, Jul 2024) | No confirmed de-peering event documented |
AS6939 Hurricane Electric (US) | Transit peer (RIPE BGP data) | No de-peering documented |
AS8218 Zayo Infrastructure France | Transit peer | No de-peering documented |
AS28917 Fiord Networks (LT) | Transit, Frankfurt; about 212 Aeza prefixes seen 17 Sep 2026 (Qurium) | No de-peering documented [25] |
AS31500 GlobalNet (RU) | Transit to AS210644 and AS216246 (RIPEstat, Oct 2026) | Russian carrier; no lever [27] |
| DataPacket | Former European transit | Terminated 24 to 31 July 2024 after the Qurium Doppelganger investigation; replaced by aurologic by early August 2024 [25] |
Following the 2024 Qurium/CORRECTIV investigations, "several transit providers decided to terminate connection to the exposed structures" (Qurium via detector.media, April 2025); specific providers were not named. The most significant documented disruption was not a de-peering but the post-sanctions IP migration from AS210644 to AS211522 (Hypercore) beginning 20 July 2025, nineteen days after the OFAC designation. aurologic continued to provide transit through at least October 2026 and remains the single most powerful upstream in RIPEstat neighbour data. The only confirmed de-peering is DataPacket in late July 2024 (Qurium). This subsection is retained per schema even where de-peering evidence is partial. [10][11][25][27]
Resilience Techniques
- Rapid ASN registration: AS211522 (Hypercore) allocated 10 Jul 2025, nine days after sanctions, with 2,100+ IPs within ten days. [10]
- Front-company rotation to hold IP space and RIPE registration independent of the Russian parent; reversed in 2026, when AS210644 was re-registered to the Russian parent's own RIPE NCC LIR record (created 29 December 2025) after the UK fronts were designated and dissolved. [27]
- Leased address space from a wide set of LIRs and IP brokers (21 referencing maintainers on the RIPE org record; Qurium names eleven suppliers holding two-thirds of the space), so no single supplier is a chokepoint. [25][27]
- Reseller abstraction insulating core ASNs from direct attribution.
- Multi-jurisdiction incorporation (RU, UK, Serbia, Uzbekistan).
- Anti-DDoS on all plans; Gast linked to botnet-based DDoS capability.
- Anonymous payment methods (crypto, QIWI, PerfectMoney, YouMoney) reducing KYC trails.
Hosted Activity Types
| Activity | Evidence Basis | Status | IOCs / Examples |
|---|---|---|---|
| Meduza Stealer C2 | OFAC; TRM Labs; ThreatFox IOC 1368443 | Confirmed | 147.45.78[.]8:80 (AS210644, first seen 2024-12-25) |
| Lumma Stealer C2 | OFAC; Qurium/CORRECTIV; The Record | Confirmed | Attributed via Qurium analysis |
| RedLine infostealer panels | OFAC press release; CyberScoop | Confirmed | Hosted RedLine panels |
| Rhadamanthys Stealer C2 | AbuseIPDB; ThreatFox | Confirmed | 91.103.252[.]25 (AS210644), reported 39× |
| RecordBreaker C2 | ThreatFox IOC 842374 | Confirmed | 89.208.103[.]4 (AS210644, 2022-08-10) |
| BianLian ransomware | OFAC press release; CyberScoop | Confirmed | Hosted BianLian infrastructure |
| BlackSprut darknet drug market | OFAC; RU court; Mash/Fontanka; Qurium | Confirmed | Hosted 2023-2025; BS2site.at |
| Doppelgänger disinformation (SDA) | Qurium/EU DisinfoLab; CORRECTIV; The Record; UK sanctions | Confirmed | 300+ prefixes, 100,000+ IPs; Liber Systems domains |
| Cobalt Strike C2 | Recorded Future / Insikt (Nov 2025 aurologic report) | Credible | Via aurologic-hosted Aeza infra |
| DarkComet / QuasarRAT C2 | Recorded Future / Insikt (Nov 2025) | Credible | Aeza-associated networks on aurologic |
| Botnet / DDoS | Forum records; aeza-gang.com; OFAC (implied) | Confirmed | Gast/Penzev botnets; DDoS since MskHost era |
| Mystic Stealer C2 (via Shelter LLC) | aeza-gang.com; Shelter LLC attribution | Credible | Shelter LLC (AS211409) |
Blocklist Standing
| Blocklist | Status | Detail |
|---|---|---|
| Spamhaus ASN-DROP (AS210644) | Listed | "This ASN should not be routed or peered with. It is under control of cyber-criminals." Confirmed via ThreatFox ASN report and Spamhaus DROP. [16][23] |
| Spamhaus ASN-DROP (AS216246) | Unknown | Not explicitly confirmed in available sources; likely but unverified. |
| Spamhaus SBL | Listed (per-IP) | Individual AS210644 IPs listed; LetHost/ZeroHost subnets flagged pre-2024. |
| ThreatFox (abuse.ch) | Listed | 3,000+ IOCs mapped to AS210644 over 12 months; Meduza, Rhadamanthys, RecordBreaker and others. [16] |
| URLhaus (abuse.ch) | Listed (per-IP) | Individual AS210644 IPs; no aggregate ASN figure confirmed. |
| Feodo Tracker (abuse.ch) | Not Applicable | Feodo datasets largely empty post-Operation Endgame; tracks Emotet/Dridex/QakBot, not the stealers Aeza hosts. |
| MalwareBazaar (abuse.ch) | Not Confirmed | No aggregate ASN-level linkage confirmed in this pass. |
| Firehol Level 1 / 2 | Probable | Likely given ASN-DROP status; not directly confirmed. |
| AbuseIPDB | Listed (per-IP) | 91.103.252[.]25 confirmed; tagged C2/stealer. |
Delisting history: No documented delisting attempts or successful delistings. Aeza's stated position was that complaints were forwarded to clients; no documented engagement with Spamhaus delisting procedures for the ASN-DROP entry. [16]
Known Weaknesses and Single Points of Failure
- aurologic dependency: the entire European delivery path transits aurologic GmbH; coordinated pressure would sever the European footprint. aurologic resisted through November 2025 citing "infrastructure neutrality." [11]
- UK corporate registration: successive UK shells (Aeza International, Hypercore, AEZATRADE, QWINS) are Companies House entities subject to UK OFSI designation, which acted rapidly in November 2025.
- Russian operator vulnerability: all confirmed operators are Russia-based nationals; three founders are in pre-trial detention.
- TRON wallet exposure: the designated TRON address was publicly identified; successor payment channels (Zakirov-established) are not yet publicly traced.
- IP-space visibility: ASN-DROP makes AS210644 ranges trivially blockable at BGP by any network implementing Spamhaus DROP feeds. [16][23]
Financial Infrastructure
Payment Methods
Advertised methods included Bitcoin, USDT (TRC20/BEP20/ERC20/TON), Litecoin, Dogecoin, BTC Cash, ETH, SOL, BNB, TRX, TON, USDC; bank cards ("of any country"); PayPal (via support); and the Russian e-wallets QIWI, YouMoney (formerly Yandex.Money), and PerfectMoney. WebMoney and SteamPay were observed in third-party reviews. Forum users noted that Russian-only payment methods carried low fees while international methods carried ~10% fees, interpreted as evidence that operations were financially centered in Russia. [18][14]
Designated Cryptocurrency Address
| TRON (TRX) Address | TU4tDFRvcKhAZ1jdihojmBWZqvJhQCnJ4F |
|---|---|
| Designated | 1 July 2025 (OFAC SDN List) |
| Attribution | OFAC; Chainalysis; TRM Labs |
| Volume received | Over $350,000 USD |
Three-Phase Laundering Model
Source: Chainalysis and TRM Labs analyses of the designated TRON address (1 July 2025). [7][8]
Phase 1 - Acquisition: Aeza used an intermediary payment processor to receive hosting fees, obscuring direct traceability. The designated TRON address functioned as an administrative/cash-out wallet rather than the primary customer-facing deposit address, so total inflow is likely larger than the $350,000 visible. Direct payments from infostealer vendors matched Aeza service pricing; regular payment pathways ran through Garantex (per TRM Labs).
Phase 2 - Layering: Funds routed through intermediary addresses before cash-out. Garantex (OFAC-sanctioned March 2025, disrupted by US/Germany/Finland) served as a layering node. Chainalysis also noted connections to "an escrow service used for selling items on a popular gaming platform," an unusual pattern that may represent deliberate obfuscation using legitimate-seeming transaction flows.
Phase 3 - Extraction: Regular cash-out points to global cryptocurrency exchanges and payment-service providers. Chainalysis Reactor graphs showed deposit addresses receiving funds from multiple sources including Garantex and an infostealer vendor. No OTC broker relationships were specifically documented in available public sources.
Post-sanctions payment infrastructure: per OFAC (19 Nov 2025), Ilya Zakirov "helped establish new companies and payment methods to obfuscate Aeza's continuing activity." Specific successor addresses are not yet publicly documented. [2]
Sanctions and Risk Designations
- Garantex: OFAC-sanctioned April 2022; disrupted March 2025; operators indicted (E.D. Va.). Aeza flows confirmed to transit Garantex. [8]
- TRON address: on the OFAC SDN List since 1 July 2025.
- No VASP-level designation specifically for Aeza's payment processor has been identified.
Client Profile and Hosted Operations
Crimeware Verticals by Evidence Tier
| Client Category | Evidence Basis | Classification |
|---|---|---|
| Meduza Stealer operators | OFAC; TRM Labs; ThreatFox (147.45.78[.]8) | Confirmed |
| Lumma Stealer operators | OFAC; Qurium; The Record; CORRECTIV | Confirmed |
| RedLine Stealer operators | OFAC; CyberScoop | Confirmed |
| Rhadamanthys Stealer operators | ThreatFox; AbuseIPDB (91.103.252[.]25) | Confirmed |
| BianLian ransomware | OFAC; CyberScoop | Confirmed |
| BlackSprut darknet drug market | OFAC; RU court; Qurium; media | Confirmed |
| Doppelgänger disinformation (SDA client) | UK sanctions; Qurium; CORRECTIV; EU DisinfoLab | Confirmed |
| DDoS operations (Aeza-originated) | Forum records; aeza-gang.com | Confirmed |
| Cobalt Strike C2 | Recorded Future / Insikt (Nov 2025) | Credible |
| DarkComet / QuasarRAT C2 | Recorded Future / Insikt (Nov 2025) | Credible |
| Mystic Stealer C2 (via Shelter LLC) | aeza-gang.com | Credible |
| Carding / RAT hosting (via LetHost/ZeroHost) | LowEndTalk; researcher accusation ("Dessgun") | Credible |
Client Geography and Target Profile
Aeza's infrastructure was physically distributed across Western Europe (Germany, Sweden, Netherlands, Finland, Austria) while operator leadership was exclusively Russian (St. Petersburg), creating a deliberate jurisdictional split: European server locations gave reduced latency for European/US-targeted campaigns while operator liability remained in Russia, where enforcement was absent until 2025. No confirmed CIS exclusion policy is documented, though Aeza's marketing emphasized service to Russian users evading censorship. [1][14]
Notable Hosted Cases
Case 1 - BlackSprut Darknet Drug Market (2023-2025)
Primary infrastructure host and anti-DDoS backbone. BlackSprut was described as one of the world's largest darknet marketplaces; Jan-Sep 2025 transaction volume was estimated at $1.85 billion. OFAC: "Aeza Group has also hosted … BlackSprut, a Russian darknet marketplace for illicit drugs." Gast "oversaw the technical details of placing Blacksprut on Aeza Group infrastructure." Bozoyan and Penzev were arrested Feb/Apr 2025 and charged under Articles 210 and 228.1 (up to 20 years). [1]
Case 2 - Meduza and Lumma Infostealers (2023-2025)
C2 hosting and IP provisioning via Aeza International (UK). OFAC: these operators "used the hosting service to target the U.S. defense industrial base and technology companies." Lumma infected ~10 million systems before its May 2025 takedown. IOC: 147.45.78[.]8:80 (Meduza C2, AS210644). OFAC: "Aeza International serves as a front company to lease IP addresses to cybercriminals, including Meduza infostealer operators." [1]
Case 3 - Doppelgänger Disinformation (2022-2025)
Core European infrastructure hub hosting fake sites impersonating Der Spiegel, The Guardian, Le Monde and others across 10+ countries. The Record (July 2024): "At the core of Doppelgänger's operation in Europe and Russia is a company called Aeza." UK FCDO designated Aeza for "provision of 'bulletproof hosting services' to the Social Design Agency (SDA)." Qurium scale: 300+ prefixes, 100,000+ IPs, ~€5M market value, ~€50,000/month leasing cost - "can only be sustained by serious financial support from external actors." [5][12][13]
Case 4 - BianLian Ransomware
Infrastructure host for the double-extortion group. Confirmed by OFAC and CyberScoop; no specific IPs or timeframes documented in open sources. [1][22]
State Nexus Assessment
The evidence supports Tier 3. The state is assessed to have been aware of operations, to have benefited from the Doppelgänger campaign, and to have refrained from enforcement of the cyber/disinformation functions for an extended period. The documented bulletproof-hosting relationship with the Social Design Agency (SDA), a Kremlin-directed entity, constitutes deliberate enablement beyond passive tolerance. Overall confidence: MODERATE-HIGH.
Positive Evidence
- Direct SDA client relationship (strongest indicator): UK FCDO confirmed Aeza "provided 'bulletproof hosting services' to the Social Design Agency (SDA)," an entity "tasked and funded directly by the Russian State" implementing campaigns "at the direction of the Russian Presidential Administration." [5]
- Doppelgänger financing scale: 300+ prefixes, 100,000+ IPs, ~€50,000/month "can only be sustained by serious financial support from external actors" (Qurium/EU DisinfoLab). [12]
- Wagner Center co-location: Aeza's St. Petersburg office was in a building that served as the Wagner Center until 2023. No direct evidentiary link between Aeza and Wagner structures has emerged; geographic co-location is noted only.
- Selective non-enforcement: Aeza operated with apparent impunity in Russia for ~4 years (2021-2025) despite public BPH documentation; Russian action came only via narcotics law (BlackSprut), not cybercrime or malicious-infrastructure hosting.
- Timing: analysts have questioned whether the arrests represent genuine law enforcement or internal reorganization of the security apparatus (aeza-gang.com). [15]
Negative Evidence and Limitations
- No confirmed direct state control: no evidence that operators are FSB/GRU/SVR personnel or that the entity is state-operated. It presents as a commercially motivated criminal enterprise that accepted state-adjacent clients (SDA) among a broader portfolio.
- Genuine RU criminal jeopardy: the arrests of Bozoyan and Penzev are inconsistent with an entity under active state protection, though the charges relate to narcotics, not the cyber/disinformation activity of primary interest.
- Penzev's public "apolitical" claims: more consistent with plausible-deniability commercialism than a witting state asset (not conclusive).
- EU non-action: the absence of any EU sanctions despite servers in Germany, Sweden, and the Netherlands is notable; drivers are not determinable from available evidence.
| Nexus Tier | Assessment |
|---|---|
| Direct Control | Not assessed - no evidence |
| Probable Cooperation | ASSESSED - SDA relationship confirmed; Doppelgänger scale; ~4-year non-enforcement |
| Tolerated Safe Harbor | Applicable as baseline - authorities demonstrably aware and non-reactive to cyber/disinfo functions |
| No Nexus | Rejected - the SDA relationship alone eliminates this |
Law Enforcement and Regulatory Response
Arrests, Sanctions, and Seizures
Three founders (Bozoyan, Penzev, Gast) were arrested and remain in Russian pre-trial detention on narcotics/organized-crime charges. Sanctions span three authorities (US, UK, Australia) across two rounds. No infrastructure seizure by any EU member state has been documented; European capacity at aurologic, Hetzner and leased LIR space was still growing in October 2026. No trial outcome or sentence for the detained founders was located in open sources as of 29 October 2026. [1][2][5][14][25][27]
Post-Disruption Client Migration
The dominant post-disruption pattern was provider-side infrastructure migration rather than client dispersal: AS210644 IP space shifted to Hypercore's AS211522 within days of sanctions, and successor shells were stood up in Serbia and Uzbekistan. Recorded Future characterized Aeza as "one of the most significant sources of malicious infrastructure" as recently as November 2025, indicating clients largely followed the migrated infrastructure rather than abandoning it. In 2026 the migration reversed: Hypercore was dissolved and unrouted, and the space returned to AS210644 and AS216246 or moved to NetCrafters OÜ, so clients never had to leave the operator. [10][11][25][27]
Connected Groups and Ecosystem Relationships
Each connected-entity claim carries two independent confidence tiers: Tier 1 (infrastructure relationship: did Aeza host their infrastructure?) and Tier 2 (operational relationship: did the Aeza operator know the client's identity or coordinate operationally?). Aeza's no-KYC, reseller-mediated model makes most Tier 2 assessments inference-level, with the notable exceptions of BlackSprut and the SDA, where OFAC/UK evidence indicates operator-level knowledge.
Vendor Attribution Summary
Corroborating vendors across the profile: OFAC, UK FCDO, Australia DFAT, Chainalysis, TRM Labs, Silent Push, Recorded Future/Insikt, Qurium, EU DisinfoLab, CORRECTIV, The Record, abuse.ch (ThreatFox/URLhaus), AbuseIPDB. No public vendor has issued an assessment materially disagreeing with the Aeza-BPH attribution. Vendors that have not published a formal Aeza-specific assessment in this pass: Mandiant, CrowdStrike, Secureworks, Microsoft MSTIC, Team Cymru.
Trajectory Assessment
Infrastructure Churn
Churn is assessed HIGH and deliberate. The defining event was the rapid post-sanctions migration of ~2,100 IPs from AS210644 to the newly allocated AS211522 (Hypercore) within nineteen days, described by Silent Push as "unusually rapid," accompanied by shared-prefix announcement (83.147.192.0/24) confirming continuity. Successor shells were stood up across three jurisdictions (UK, Serbia, Uzbekistan). The second phase, after the November 2025 designations, ran the other way: Hypercore dissolved and went dark (Dec 2025 to Feb 2026), AS210644 was re-homed to the Russian parent's own RIPE LIR record (Mar 2026), former Hypercore space moved to NetCrafters OÜ (Feb 2026), and 57 new IPv4 blocks were registered between July 2025 and October 2026. [10][25][27]
Market Position
Aeza was a large-scale, established BPH operator (~100,000+ IPs at peak) serving a broad portfolio spanning infostealers, ransomware, a major darknet market, and state-aligned disinformation. Recorded Future's November 2025 characterization as "one of the most significant sources of malicious infrastructure" indicates it retained material market weight even after sanctions. Qurium's September 2026 count (about 137,000 addresses, roughly twenty times the 2022 baseline and above the pre-sanctions estimate) shows the footprint has grown, not shrunk, under two rounds of sanctions. [11][25]
Disruption History
Three disruption vectors converged in 2025: Russian criminal arrests (Feb/Apr), tri-lateral sanctions (Jul and Nov), and infrastructure exposure by researchers (Silent Push, Recorded Future, Qurium). None fully terminated operations; the group adapted via migration and rebranding. The EU imposed no sanctions and no server seizures are documented. Reconstitution signals per the RIPE maintainer method: 57 IPv4 blocks registered after the OFAC action, in six clusters, the most recent on 13 October 2026; one direct RIPE NCC IPv6 allocation (object March 2026); and a RIPE NCC LIR record for the sanctioned parent created five weeks after the second designation round. [27]
Aeza is assessed as active and expanding. Sanctions froze US-nexus assets, blocked the designated wallet and removed the UK fronts; three founders remain detained. None of that touched the infrastructure layer: address space is leased from a dozen LIRs and brokers, routed by the original two ASNs plus NetCrafters, carried by aurologic, and registered through a RIPE NCC membership the sanctioned parent obtained after designation. The EU has not designated Aeza, and RIPE NCC (a Dutch association bound by EU, not US, sanctions) is therefore not obliged to freeze the registrations. Analyst Inference The three levers that would change the trajectory are, in order: an EU designation (which would bind RIPE NCC, aurologic, Hetzner and the EU-based LIRs at once), aurologic de-peering (the single dominant upstream of both AS210644 and AS203273), and supplier-side action by the LIRs named by Qurium. Absent those, expect continued monthly block registrations and further shell rotation.
Mandatory Intelligence Gaps
Identities and scale of downstream resellers beyond LetHost, ZeroHost, and TNSecurity are unknown.
Specific crypto addresses and payment methods established by Zakirov after November 2025 are not publicly identified.
Hypercore is dissolved and unrouted. Smart Digital Ideas DOO (AS215829) and Datavice MCHJ (AS206336) routing status was not re-checked this pass. NetCrafters OÜ's relationship to Aeza (controlled vs lessee) is unresolved.
No verdict, sentence or release for Penzev, Bozoyan or Gast located in open sources as of 29 October 2026; Russian court records not queried.
16 of 58 post-sanctions /24s (June 2026 Moscow and Stockholm blocks, all Sep to Oct 2026 blocks) await AbuseIPDB check-block after the free-tier daily cap; ThreatFox and URLhaus coverage is complete.
No EU member state has seized Aeza-associated servers; current status of hardware at aurologic/Hetzner is undocumented.
The non-arrested 33% owner's whereabouts and legal status post-sanctions are unconfirmed.
SDA's state-funded status is confirmed, but the specific funding flows to Aeza are not publicly documented.
Open reporting names "Patryk Drozda" as Hypercore's registrant and records dissolution on 23 December 2025; both remain single-source and not corroborated against Companies House directly in this pass.
Only AS210644 is explicitly confirmed ASN-DROP listed; per-IP SBL history for AS216246 is unconfirmed.
Recent Reporting
Update Pass (29 October 2026)
RIPE database and RIPEstat queries run for this pass, together with Qurium's 14 October 2026 report, show that Aeza's infrastructure footprint is larger than at any point before sanctions: 316 and 58 IPv4 prefixes on AS210644 and AS216246, 171 on NetCrafters AS203273, about 137,000 addresses in September 2026 against roughly 100,000 pre-sanctions and 6,400 in 2022. The Hypercore successor (AS211522) is dissolved and unrouted since 7 February 2026. The RIPE maintainer footprint shows 57 IPv4 blocks registered after the July 2025 OFAC action (latest 13 October 2026), a direct RIPE NCC IPv6 allocation, and a RIPE NCC LIR organisation record for AEZA GROUP LLC created 29 December 2025. No EU designation, arrest, seizure or trial outcome was identified. The "Degraded but Persistent" assessment of July 2026 is withdrawn. [25][26][27]
Follow-On Verification (July 2026)
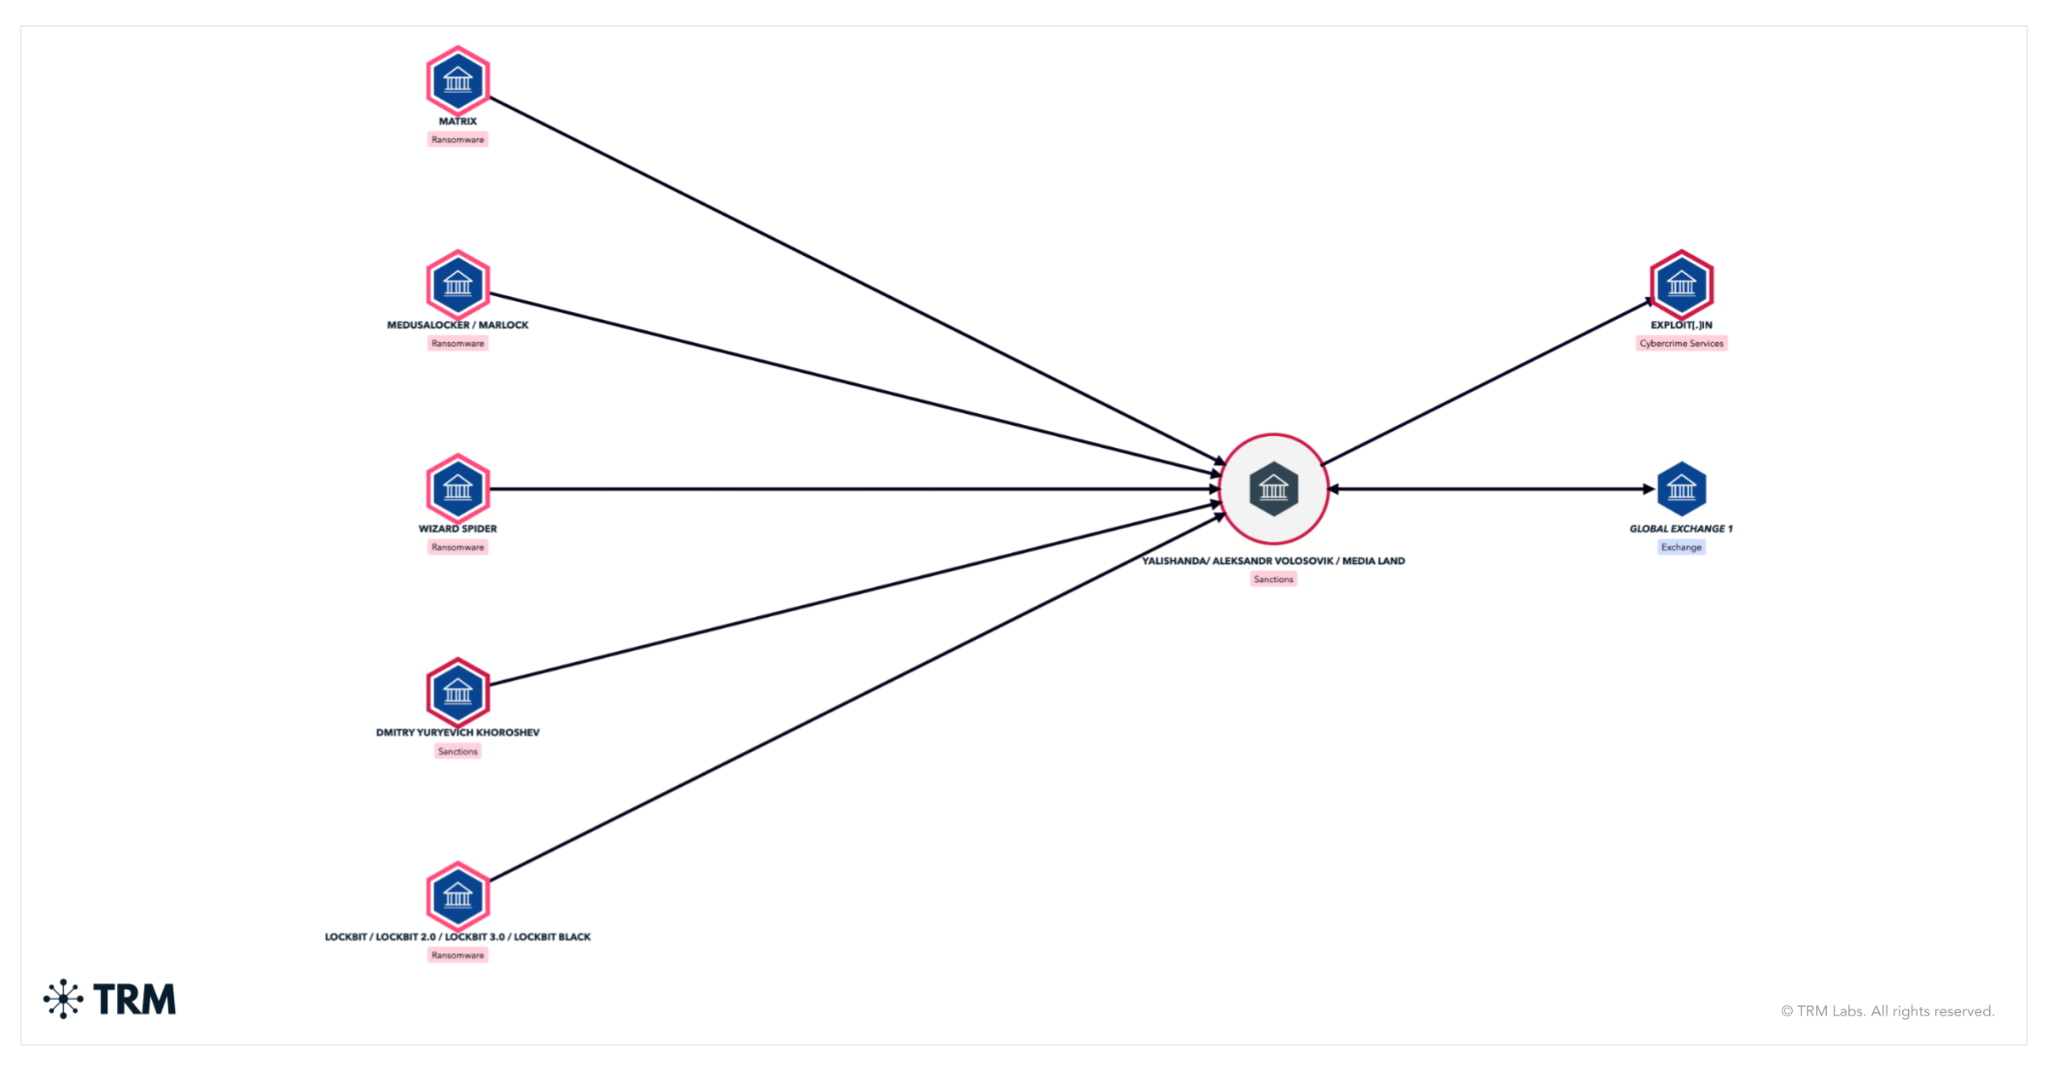
This profile's core claims were verified against primary sources during a July 2026 follow-on pass. The OFAC July 2025 press release (SB0185) was confirmed verbatim for hosted-activity attributions (Meduza, Lumma, RedLine panels, BianLian, BlackSprut) and personnel roles. The November 2025 tri-lateral action (SB0319) was confirmed to have designated Hypercore Ltd plus Serbian/Uzbek successors and operators Makarov and Zakirov (note: SB0319 also designated the separate Media Land / Yalishanda BPH network, which is a distinct EDP node). The AS210644→AS211522 migration and AS211522 allocation date were corroborated via Silent Push and BGP data.
No EU designation, additional arrest, indictment, or infrastructure seizure specific to Aeza was identified in open sources for January-July 2026. The EU's continued non-action (despite European hosting) remains the most notable outstanding anomaly. Status is assessed unchanged from the December 2025 VSquare reporting.
Secondary reporting attributes Hypercore Ltd's registration to "Patryk Drozda" two days after the July 2025 sanctions. This name does not appear in the OFAC designation text and is treated as CREDIBLE / single-source pending Companies House corroboration. The researcher-named front person for Aeza International Ltd is separately identified as Marat Timurov (Kazakhstan), also non-designated.